What Data Can You Put in ChatGPT? A Practical Privacy Traffic Light
Public, synthetic or truly anonymized data is usually the safest; real customer, health, employee, contract, financial and access data should not go into unvetted consumer chats. OpenAI says prompts and uploads can be collected as User Content containing personal data; ChatGPT data controls mainly affect whether con...
Published byEdited with GPT-5.5Images generated with GPT Image 2
Public, synthetic or truly anonymized data is usually the safest; real customer, health, employee, contract, financial and access data should not go into unvetted consumer chats.
OpenAI says prompts and uploads can be collected as User Content containing personal data; ChatGPT data controls mainly affect whether conversations help improve models.[5][9]
OpenAI describes separate rules for ChatGPT Business, Enterprise, Edu, Healthcare and API data, including no default training on Business Data.[7]
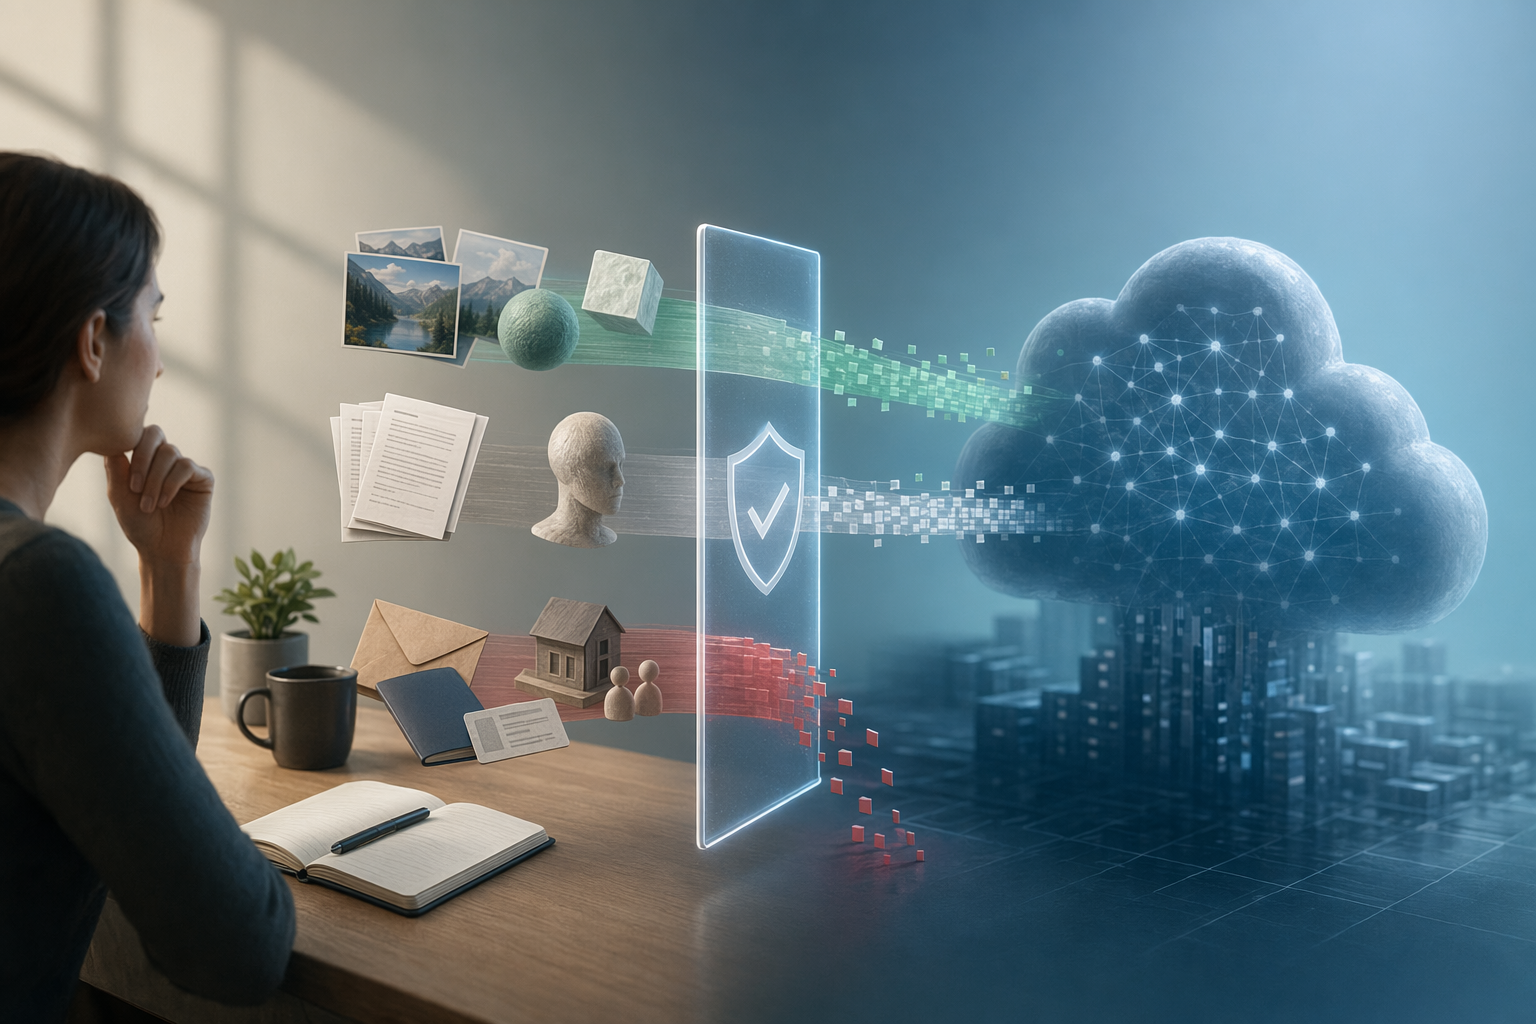
ChatGPT-Datenschutz: Welche Daten darfst du in KI-Tools eingebenKI-generiertes Symbolbild: Datenschutz-Check vor dem Upload in ChatGPT oder andere KI-Tools.
AI Prompt
Create a landscape editorial hero image for this Studio Global article: ChatGPT-Datenschutz: Welche Daten darfst du in KI-Tools eingeben?. Article summary: Gib in öffentliche KI Tools nur Daten ein, die du auch einem externen Cloud Dienst anvertrauen würdest: öffentliche, synthetische oder wirklich anonymisierte Inhalte.. Topic tags: chatgpt, openai, privacy, data protection, gdpr. Reference image context from search candidates: Reference image 1: visual subject "Embivalent" source context "Welche Daten darf / sollte ich bei welcher KI (nicht) eingeben?" Reference image 2: visual subject "Dominik Freinhofer" source context "Welche Daten darf / sollte ich bei welcher KI (nicht) eingeben?" Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, a
openai.com
The simplest rule is this: treat ChatGPT and similar AI tools like outside cloud services until they have been properly approved. Public, synthetic or genuinely anonymized material is generally lower-risk. Anything that identifies people, grants access, is contractually confidential or contains trade secrets should not be pasted into an unvetted consumer AI tool.
The reason is not just model training. OpenAI's privacy policy says it collects personal data that users provide as content in its services, including prompts and uploads such as files, images, audio and video. So the key question is broader: is this exact tool allowed to process this exact data for this exact purpose?
The privacy traffic light for ChatGPT and other AI tools
Category
Examples
Practical guidance
Green
Public information, general questions, invented examples, dummy data, synthetic datasets, truly anonymized extracts
Usually suitable, as long as no personal, confidential or protected information is included.
Yellow
Internal drafts with no secrets, anonymized support cases, code with secrets removed, spreadsheets after deleting names, IDs and contact details
Use only with data minimization, an approved tool and checked settings for training, storage and access.
Red
Passwords, API keys, tokens, login credentials, passport or tax data, bank details, health or patient data, full customer or employee records, confidential contracts, merger-and-acquisition material, unpublished financials, source code containing secrets or core intellectual property
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "What Data Can You Put in ChatGPT? A Practical Privacy Traffic Light"?
Public, synthetic or truly anonymized data is usually the safest; real customer, health, employee, contract, financial and access data should not go into unvetted consumer chats.
What are the key points to validate first?
Public, synthetic or truly anonymized data is usually the safest; real customer, health, employee, contract, financial and access data should not go into unvetted consumer chats. OpenAI says prompts and uploads can be collected as User Content containing personal data; ChatGPT data controls mainly affect whether conversations help improve models.[5][9]
What should I do next in practice?
OpenAI describes separate rules for ChatGPT Business, Enterprise, Edu, Healthcare and API data, including no default training on Business Data.[7]
Do not copy these into unvetted consumer tools. If processing is necessary, use an approved Business, Enterprise or API environment and follow internal approval rules.
This traffic light is not legal advice. It is a practical safety filter. The easier it is for a prompt, file or table to identify a person, customer, employee, patient, contract or internal system, the more conservative you should be.
Why consumer ChatGPT needs extra caution
A ChatGPT conversation is not the same as a note stored only on your laptop. OpenAI says User Content can include personal data and specifically mentions prompts and uploaded content.
ChatGPT data controls are meant to let users decide whether their conversations and interactions help improve OpenAI's models. Turning that off can be an important privacy step. But it does not automatically make sensitive content acceptable, because training is only one part of the privacy and compliance picture.
Temporary Chats reduce some risks. OpenAI describes them as not saved in chat history, not used for memories, not used to train models and deleted after 30 days; OpenAI also says they may still be reviewed for abuse monitoring. That means Temporary Chat is not a free pass for confidential business documents, real customer data or health information.
What changes with Business, Enterprise, Edu, Healthcare and API use
OpenAI distinguishes consumer use from its business-oriented products. It defines Business Data as inputs and outputs from ChatGPT Business, ChatGPT Enterprise, ChatGPT for Healthcare, ChatGPT Edu, ChatGPT for Teachers and the API Platform.
For that Business Data, OpenAI says it does not train its models by default. OpenAI also says it can execute a Data Processing Addendum for ChatGPT Business, ChatGPT Enterprise and API customers to support GDPR and other privacy-law compliance, while ChatGPT Edu and ChatGPT for Teachers are covered through a Student Data Privacy Agreement. OpenAI separately provides information on business data privacy, security, compliance and data-retention policies for Enterprise, Business, Edu, ChatGPT for Healthcare and the API Platform.
That still does not mean every upload is allowed. Organizations still need to check the purpose, data type, user permissions, retention settings, internal policies, customer contracts and any sector-specific rules before real data is processed.
Questions to ask before you upload real data
Before entering or uploading real information into an AI tool, answer these questions:
Has privacy, legal and IT approved this tool for this type of use?
Does the provider use prompts, files or outputs for training or model improvement?
Is there an opt-out setting or a contractual exclusion for training use?
How long are prompts, uploads and outputs retained?
Can people at the provider review content for support, security or abuse monitoring?
Could third-party apps, connectors, plugins or subprocessors access the content?
Are there clear controls for data processing terms, admin rights, roles, audits and retention?
Do internal policies and external contracts allow this exact data to be processed in this exact tool?
If the answers are unclear, use placeholders, anonymized excerpts or synthetic data instead.
Better prompting: minimize instead of copying everything
The safest prompt contains only what the model truly needs. Remove names, email addresses, phone numbers, postal addresses, account numbers, patient numbers, contract numbers and other identifiers when they are not essential.
Customer cases: Do not paste a full support case with a name, customer number and contact details. Use placeholders such as [CUSTOMER], [CUSTOMER_ID] and [DATE].
Spreadsheets: Do not upload complete customer or employee lists. Remove direct identifiers and include only the columns needed for the analysis.
Code: Never paste API keys, tokens, private certificates, passwords or production credentials into prompts. Share only the relevant code snippet and replace configuration values with placeholders.
Contracts and financial material: If you need help with a clause, pattern or wording, use an anonymized excerpt rather than the whole document.
If you really need to process real data
Sometimes dummy data is not enough. In that case, take the conservative route:
Clarify the purpose: Check whether the model truly needs real data or whether an anonymized excerpt will work.
Minimize the dataset: Use the smallest amount of data that can answer the question.
Remove identifiers: Reduce references to people, customers, patients and organizations as much as possible.
Delete secrets: Passwords, tokens, API keys and private certificates do not belong in prompts.
Use an approved environment: For business data, use a reviewed Business, Enterprise or API setup. OpenAI describes separate enterprise privacy commitments for these products, including no default training on Business Data.
Check settings and contracts: Confirm training use, retention, role permissions, data processing terms and deletion rules before upload.
Document the use: Record the tool, purpose, data type, settings and approval path.
Bottom line
There is no universal yes or no for ChatGPT. In consumer use, prompts and uploads can contain personal data and are collected by OpenAI as User Content. Data controls and Temporary Chats affect whether conversations help improve models, appear in history or create memories; Temporary Chats are deleted after 30 days, but may still be reviewed for abuse monitoring.
For ChatGPT Business, Enterprise, Edu, Healthcare and API use, OpenAI describes separate rules, including no default training on Business Data. When in doubt, do not paste it. Anonymize, use placeholders or move the task into an approved Business, Enterprise or API environment.
captaincompliance.comChatGPT Data Security & Privacy: The Complete Guide for Users and Enterprises - Captain Compliance