這種模式以「受控能力請求」取代硬編碼 API key,支援即時(just‑in‑time)與最小權限(least privilege)憑證,並能集中稽核與撤銷存取權。[1][5]
即使如此,企業仍需要 MCP allowlist、密鑰政策、程式碼審查與秘密掃描等防護,因為工具整合與 AI 生成程式碼仍可能帶來安全風險。[3][18]
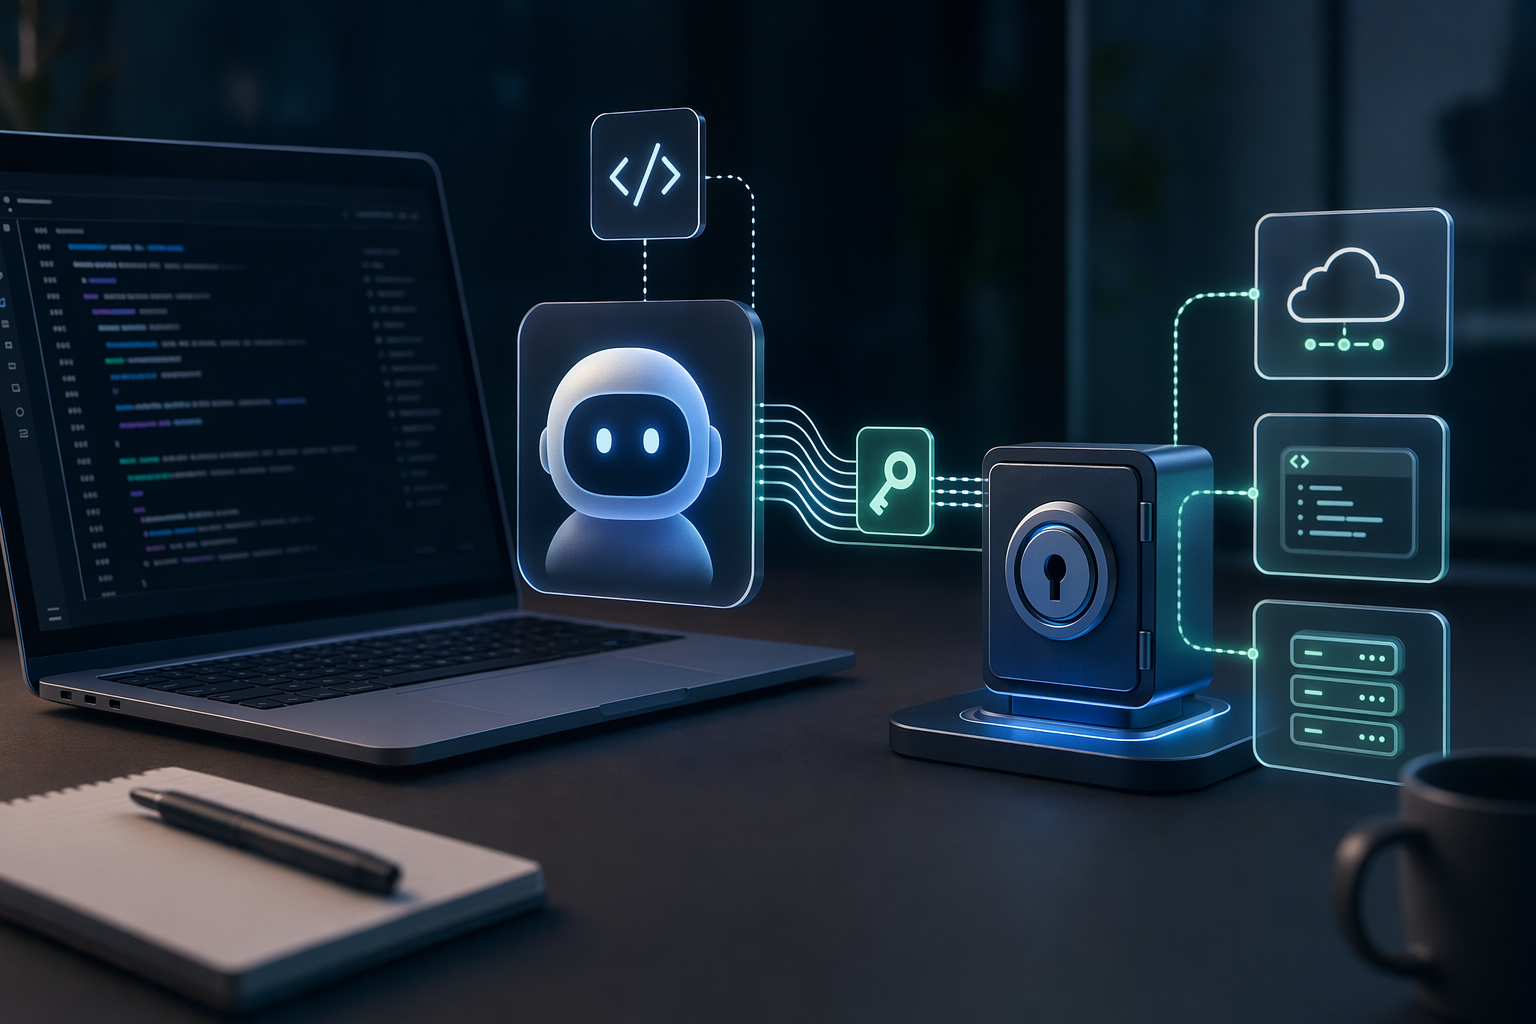
How does the new partnership between OpenAI and 1Password improve security for the Codex AI coding agent, and how does the integration workModern AI coding agents can request credentials through secure tools instead of exposing secrets directly to the model.
AI 提示詞
Create a landscape editorial hero image for this Studio Global article: How does the new partnership between OpenAI and 1Password improve security for the Codex AI coding agent, and how does the integration work. Article summary: The OpenAI–1Password pattern can improve Codex security by moving secrets out of prompts and model inputs, and instead letting Codex request narrowly scoped credentials through a mediated tool path; 1Password warns that . Topic tags: general, documentation, general web, user generated. Reference image context from search candidates: Reference image 1: visual subject "Coding agents are now writing production features on real development teams, and a new report from DryRun Security shows that those agents introduce security vulnerabilities at a h" source context "AI coding agents keep repeating decade-old security mistakes - Help Net Security" Reference image 2: v
openai.com
AI coding agent(例如 OpenAI 的 Codex)已經能寫程式、執行指令、呼叫 API,甚至自動部署應用。但一旦 AI 要在真實系統中工作,就不可避免需要憑證(credentials):API 金鑰、存取權杖、資料庫密碼或雲端服務憑證。
問題是,傳統做法往往很危險。開發者常把 API key 直接貼進 prompt、.env 檔案或設定檔。只要這些機密被送進模型的 context window,它們就可能出現在日誌、生成程式碼或其他輸出中,之後就很難再控制其流向。
OpenAI 與密碼管理平台 1Password 所採用的新整合模式,正是為了解決這個問題:讓 AI 可以使用憑證,但永遠看不到它們。
這種模式以「受控能力請求」取代硬編碼 API key,支援即時(just‑in‑time)與最小權限(least privilege)憑證,並能集中稽核與撤銷存取權。[1][5]
即使如此,企業仍需要 MCP allowlist、密鑰政策、程式碼審查與秘密掃描等防護,因為工具整合與 AI 生成程式碼仍可能帶來安全風險。[3][18]
How does the new partnership between OpenAI and 1Password improve security for the Codex AI coding agent, and how does the integration workModern AI coding agents can request credentials through secure tools instead of exposing secrets directly to the model.
AI 提示詞
Create a landscape editorial hero image for this Studio Global article: How does the new partnership between OpenAI and 1Password improve security for the Codex AI coding agent, and how does the integration work. Article summary: The OpenAI–1Password pattern can improve Codex security by moving secrets out of prompts and model inputs, and instead letting Codex request narrowly scoped credentials through a mediated tool path; 1Password warns that . Topic tags: general, documentation, general web, user generated. Reference image context from search candidates: Reference image 1: visual subject "Coding agents are now writing production features on real development teams, and a new report from DryRun Security shows that those agents introduce security vulnerabilities at a h" source context "AI coding agents keep repeating decade-old security mistakes - Help Net Security" Reference image 2: v
openai.com
AI coding agent(例如 OpenAI 的 Codex)已經能寫程式、執行指令、呼叫 API,甚至自動部署應用。但一旦 AI 要在真實系統中工作,就不可避免需要憑證(credentials):API 金鑰、存取權杖、資料庫密碼或雲端服務憑證。
問題是,傳統做法往往很危險。開發者常把 API key 直接貼進 prompt、.env 檔案或設定檔。只要這些機密被送進模型的 context window,它們就可能出現在日誌、生成程式碼或其他輸出中,之後就很難再控制其流向。
OpenAI 與密碼管理平台 1Password 所採用的新整合模式,正是為了解決這個問題:讓 AI 可以使用憑證,但永遠看不到它們。
agentpatterns.aiSecrets Management for AI Agents: Credential Injection
developer.1password.comhttps://developer.1password.com/llms-sdks.txt
1password.devSecure AI access - 1Password Developer Tools
developers.openai.comModel Context Protocol – Codex | OpenAI Developers