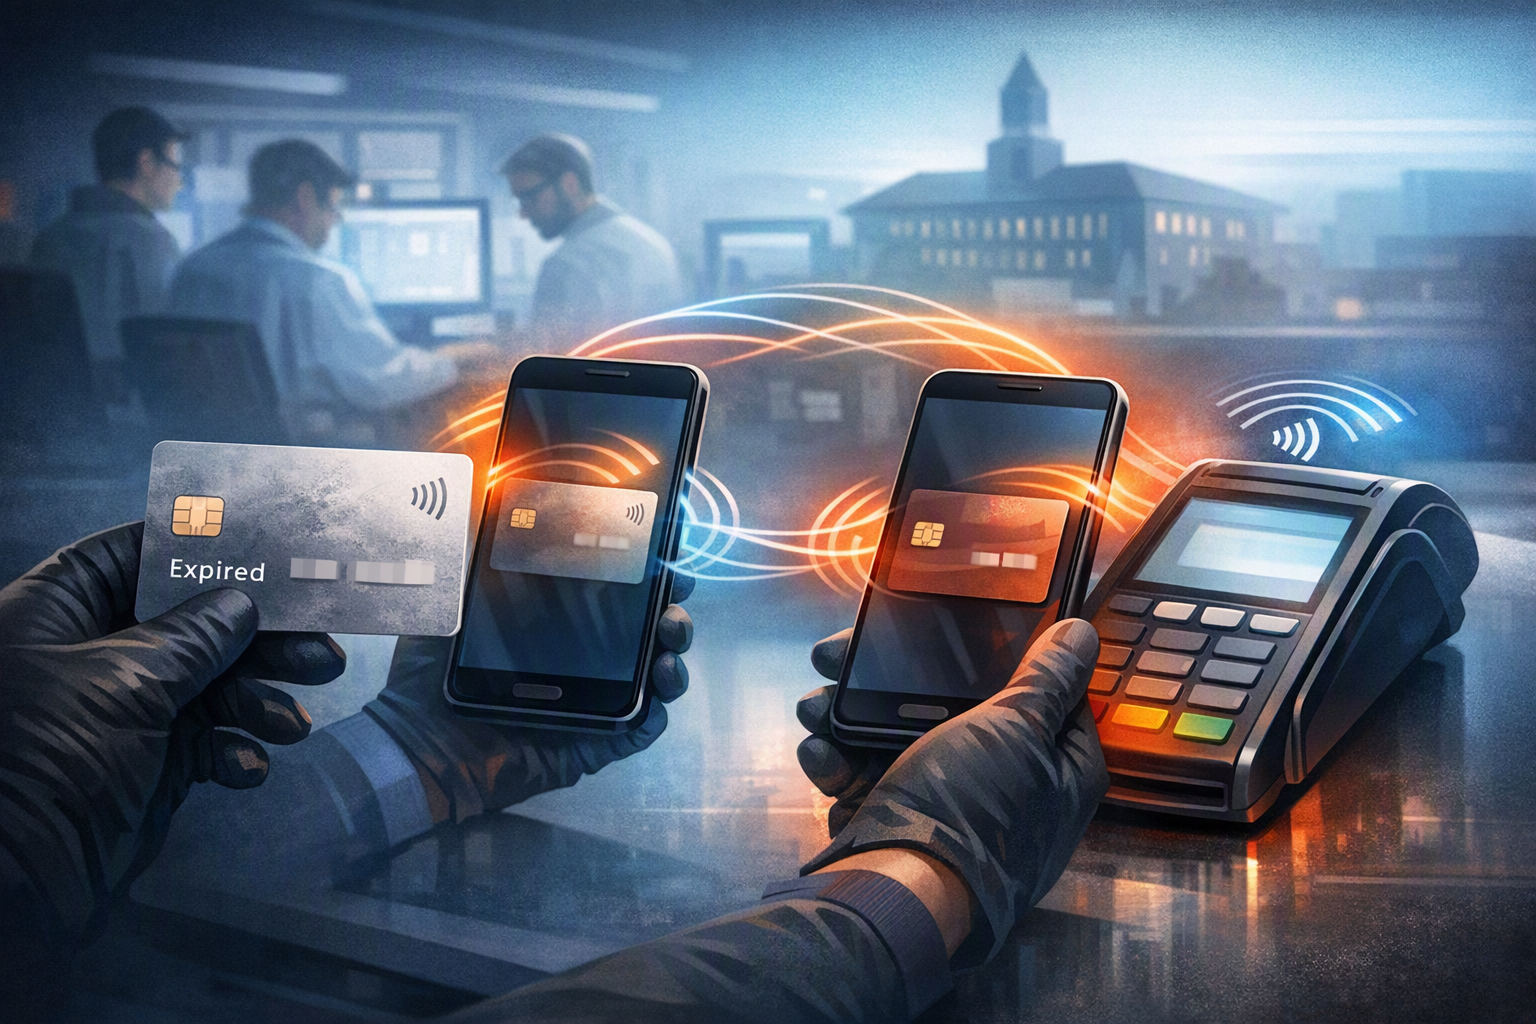
What is the “Zombie Card” NFC relay attack demonstrated by University of Massachusetts Amherst researchers at the 35th USENIX Security SympoConceptual illustration of the two-phone NFC relay described in the Zombie Card research.
AI 提示
Create a landscape editorial hero image for this Studio Global article: What is the “Zombie Card” NFC relay attack demonstrated by University of Massachusetts Amherst researchers at the 35th USENIX Security Sympo. Article summary: “Zombie Card” is a practical NFC man-in-the-middle relay attack: two ordinary smartphones relay an expired physical contactless card to a point-of-sale terminal while altering the expiration date the terminal sees. It do. Topic tags: general, general web. Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, and topical grounding; do not copy the exact image. Avoid: logos, brand marks, copyrighted characters, real person likenesses, fake screenshots, UI text, readable text, watermarks, charts with fake numbers, clic
现有证据不足以逐一确认这三个内核在协议层面究竟依靠哪条具体规则阻止攻击。因此,更稳妥的结论是:研究中演示的“篡改有效期”方法对测试中的 Visa 支付路径有效,但在测试的 Mastercard、American Express 和 Discover 路径上没有复现成功。这并不能证明 Visa 卡普遍可以被伪造,也不意味着每一张过期 Visa 卡都一定能继续付款。
现有证据不足以逐一确认这三个内核在协议层面究竟依靠哪条具体规则阻止攻击。因此,更稳妥的结论是:研究中演示的“篡改有效期”方法对测试中的 Visa 支付路径有效,但在测试的 Mastercard、American Express 和 Discover 路径上没有复现成功。这并不能证明 Visa 卡普遍可以被伪造,也不意味着每一张过期 Visa 卡都一定能继续付款。
xenospectrum.comAttack Revives Expired Credit Cards Using Two Smartphones | XenoSpectrum
theregister.comExpired credit cards revived by researchers to make ...
khwarizmilab.github.ioZombie Cards Back Online: Expired Card Attack - Khwarizmi Lab
cybersecuritynews.comNew “Zombie Card” Flaw Lets Expired Visa Cards Make Contactless Payments