企业应优先修补 BIG‑IP 与 Linux 内核漏洞、限制边界设备 shell 访问、禁用高风险内核模块并监控提权与横向移动行为。
How are hackers chaining vulnerabilities in internet‑facing F5 BIG‑IP appliances with Linux privilege‑escalation bugs like CopyFail (CVE‑202Modern enterprise intrusions often begin at exposed edge appliances before escalating privileges and pivoting deeper into internal systems.
AI 提示
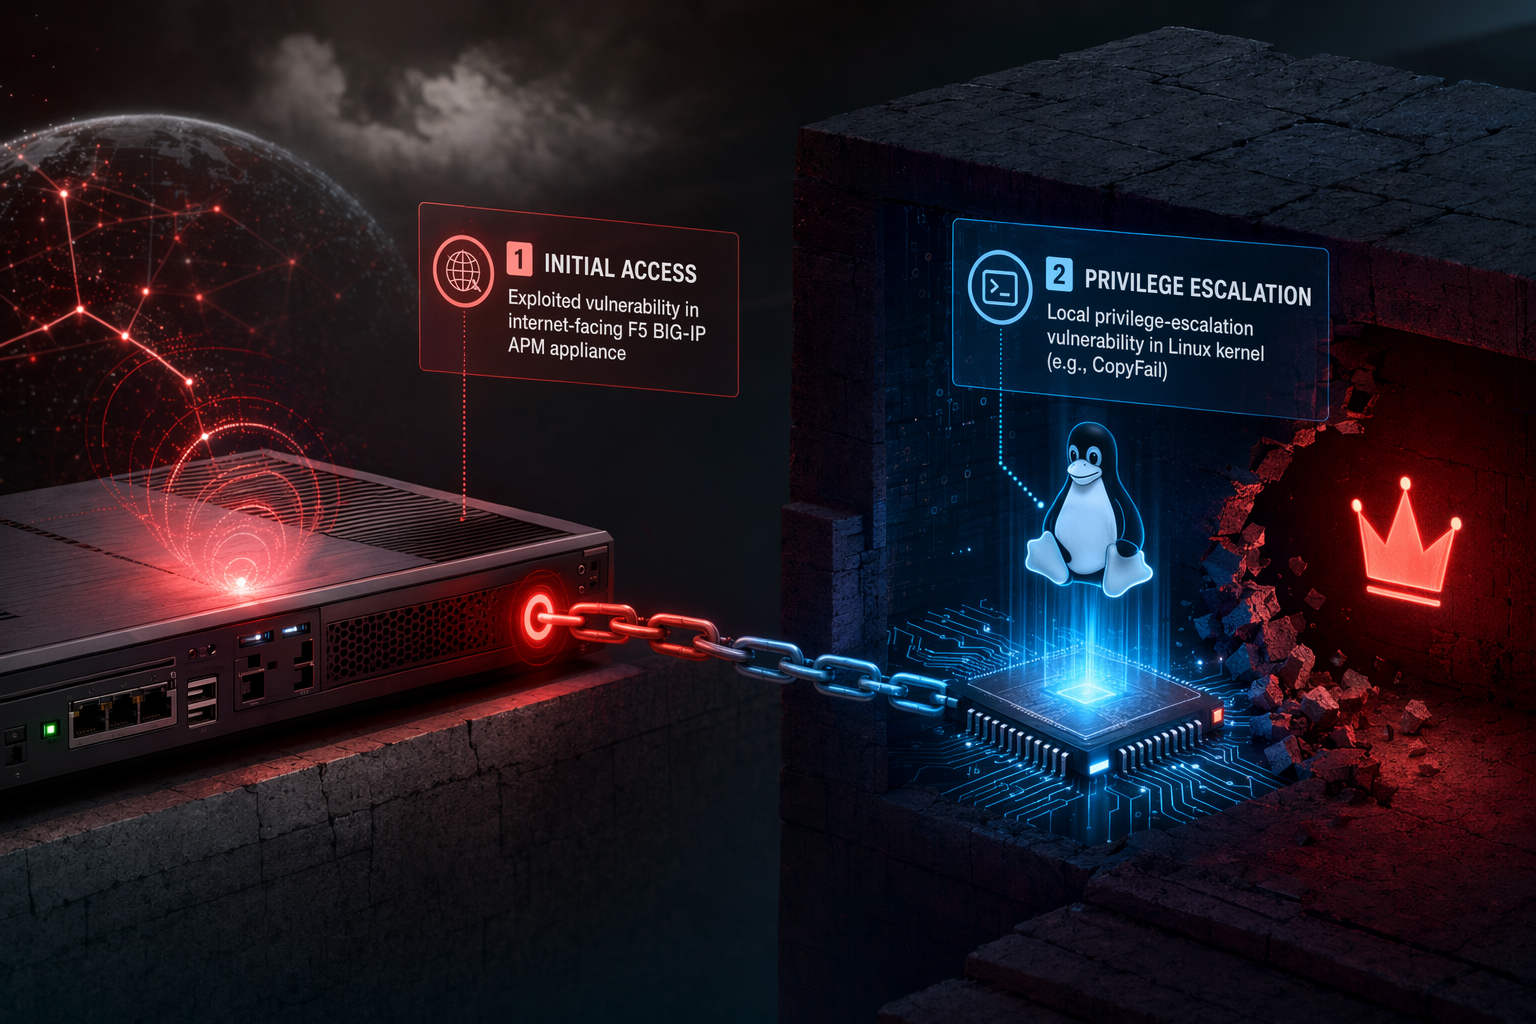
Create a landscape editorial hero image for this Studio Global article: How are hackers chaining vulnerabilities in internet‑facing F5 BIG‑IP appliances with Linux privilege‑escalation bugs like CopyFail (CVE‑202. Article summary: Hackers are reportedly using a two-step chain: first they gain initial access on exposed F5 BIG‑IP APM devices through a remotely exploitable flaw such as CVE‑2025‑53521, then they use Linux local privilege-escalation bu. Topic tags: general, government, education, documentation, general web. Reference image context from search candidates: Reference image 1: visual subject "A local privilege escalation (LPE) vulnerability, dubbed Copy Fail (CVE-2026-31431), has been identified in the Linux kernel's `authencesn` cryptographic template. This logic flaw" source context "Weekly Threat Bulletin – May 6th, 2026 | F5 Labs" Reference image 2: visual subject "# CVE-2026
openai.com
企业网络攻击正在出现一个越来越常见的模式:先攻破互联网暴露的边界设备,再利用 Linux 内核漏洞完成提权,最后横向进入企业内部系统。
企业应优先修补 BIG‑IP 与 Linux 内核漏洞、限制边界设备 shell 访问、禁用高风险内核模块并监控提权与横向移动行为。
How are hackers chaining vulnerabilities in internet‑facing F5 BIG‑IP appliances with Linux privilege‑escalation bugs like CopyFail (CVE‑202Modern enterprise intrusions often begin at exposed edge appliances before escalating privileges and pivoting deeper into internal systems.
AI 提示
Create a landscape editorial hero image for this Studio Global article: How are hackers chaining vulnerabilities in internet‑facing F5 BIG‑IP appliances with Linux privilege‑escalation bugs like CopyFail (CVE‑202. Article summary: Hackers are reportedly using a two-step chain: first they gain initial access on exposed F5 BIG‑IP APM devices through a remotely exploitable flaw such as CVE‑2025‑53521, then they use Linux local privilege-escalation bu. Topic tags: general, government, education, documentation, general web. Reference image context from search candidates: Reference image 1: visual subject "A local privilege escalation (LPE) vulnerability, dubbed Copy Fail (CVE-2026-31431), has been identified in the Linux kernel's `authencesn` cryptographic template. This logic flaw" source context "Weekly Threat Bulletin – May 6th, 2026 | F5 Labs" Reference image 2: visual subject "# CVE-2026
openai.com
企业网络攻击正在出现一个越来越常见的模式:先攻破互联网暴露的边界设备,再利用 Linux 内核漏洞完成提权,最后横向进入企业内部系统。
microsoft.comFrom edge appliance to enterprise compromise: Multi-stage Linux ...
ncsc.gov.ukVulnerability affecting F5 BIG-IP APM | National Cyber Security Centre
hadrian.ioF5 BIG-IP APM Remote Code Execution: CVE-2025-53521 ...