Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน
กลไกการโจมตีใช้พร็อกซีตัวกลางระหว่างเหยื่อกับเซิร์ฟเวอร์จริงของ Microsoft เมื่อเหยื่อกรอกรหัสผ่านและผ่าน MFA สำเร็จ พร็อกซีจะขโมยคุกกี้เซสชันทันที ทำให้แฮกเกอร์สามารถเข้าถึงบัญชีได้โดยไม่ต้องผ่าน MFA อีก
แคมเปญนี้หมุนเวียนใช้ชุดฟิชชิ่งอย่างน้อย 3 ตัว ได้แก่ EvilProxy, FlowerStorm และ Kali365 ซึ่งล้วนเป็นบริการ Phishing as a Service (PhaaS) ที่มีขายในตลาดมืด
Search & fact-check with cited sources for What is the new Microsoft 365 session hijacking campaign that leverages compromised Outlook mailbAdversary-in-the-middle (AiTM) phishing works by placing a proxy between the victim and the legitimate authentication service, capturing the session cookie issued after MFA.
AI พรอมต์
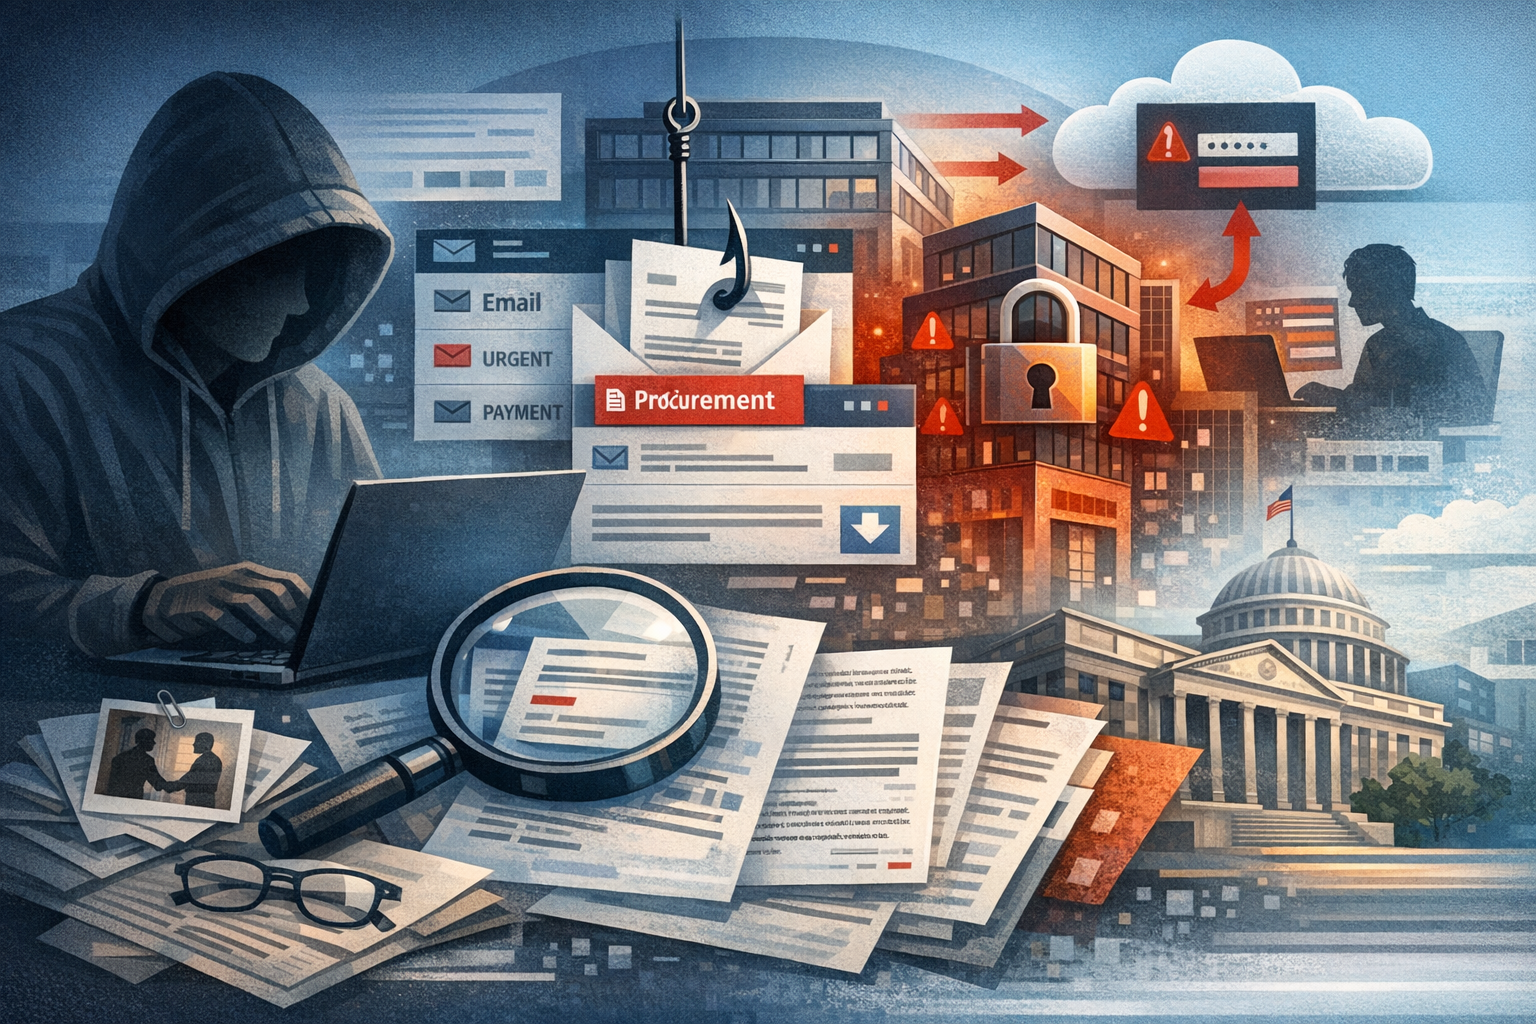
Create a landscape editorial hero image for this Studio Global article: Search & fact-check with cited sources for What is the new Microsoft 365 session hijacking campaign that leverages compromised Outlook mailb. Article summary: ## The "Procurement Trap" Campaign. Topic tags: general, general web, user generated, government. Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, and topical grounding; do not copy the exact image. Avoid: logos, brand marks, copyrighted characters, real person likenesses, fake screenshots, UI text, readable text, watermarks, charts with fake numbers, clickbait thumbnails, icons, and tiny thumbnail layouts. Make it useful as an illustrative visual, not as factual evidence.
openai.com
แคมเปญ 'กับดักจัดซื้อจัดจ้าง' (The Procurement Trap) คืออะไร?
Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน
ประเด็นสำคัญที่ต้องตรวจสอบก่อนคืออะไร?
Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน กลไกการโจมตีใช้พร็อกซีตัวกลางระหว่างเหยื่อกับเซิร์ฟเวอร์จริงของ Microsoft เมื่อเหยื่อกรอกรหัสผ่านและผ่าน MFA สำเร็จ พร็อกซีจะขโมยคุกกี้เซสชันทันที ทำให้แฮกเกอร์สามารถเข้าถึงบัญชีได้โดยไม่ต้องผ่าน MFA อีก
ฉันควรทำอย่างไรต่อไปในทางปฏิบัติ?
แคมเปญนี้หมุนเวียนใช้ชุดฟิชชิ่งอย่างน้อย 3 ตัว ได้แก่ EvilProxy, FlowerStorm และ Kali365 ซึ่งล้วนเป็นบริการ Phishing as a Service (PhaaS) ที่มีขายในตลาดมืด
Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน
กลไกการโจมตีใช้พร็อกซีตัวกลางระหว่างเหยื่อกับเซิร์ฟเวอร์จริงของ Microsoft เมื่อเหยื่อกรอกรหัสผ่านและผ่าน MFA สำเร็จ พร็อกซีจะขโมยคุกกี้เซสชันทันที ทำให้แฮกเกอร์สามารถเข้าถึงบัญชีได้โดยไม่ต้องผ่าน MFA อีก
แคมเปญนี้หมุนเวียนใช้ชุดฟิชชิ่งอย่างน้อย 3 ตัว ได้แก่ EvilProxy, FlowerStorm และ Kali365 ซึ่งล้วนเป็นบริการ Phishing as a Service (PhaaS) ที่มีขายในตลาดมืด
Search & fact-check with cited sources for What is the new Microsoft 365 session hijacking campaign that leverages compromised Outlook mailbAdversary-in-the-middle (AiTM) phishing works by placing a proxy between the victim and the legitimate authentication service, capturing the session cookie issued after MFA.
AI พรอมต์
Create a landscape editorial hero image for this Studio Global article: Search & fact-check with cited sources for What is the new Microsoft 365 session hijacking campaign that leverages compromised Outlook mailb. Article summary: ## The "Procurement Trap" Campaign. Topic tags: general, general web, user generated, government. Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, and topical grounding; do not copy the exact image. Avoid: logos, brand marks, copyrighted characters, real person likenesses, fake screenshots, UI text, readable text, watermarks, charts with fake numbers, clickbait thumbnails, icons, and tiny thumbnail layouts. Make it useful as an illustrative visual, not as factual evidence.
openai.com
แคมเปญ 'กับดักจัดซื้อจัดจ้าง' (The Procurement Trap) คืออะไร?
Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน
ประเด็นสำคัญที่ต้องตรวจสอบก่อนคืออะไร?
Infoblox เปิดเผยแคมเปญ 'The Procurement Trap' เมื่อวันที่ 22 กรกฎาคม 2026 เป็นการโจมตีแบบ AiTM ฟิชชิ่งทั่วโลก ส่งอีเมลปลอมแปลงเป็นเอกสารจัดซื้อจัดจ้าง RFI หรือใบเสนอราคา จากบัญชี Outlook ที่ถูกแฮกมาก่อน กลไกการโจมตีใช้พร็อกซีตัวกลางระหว่างเหยื่อกับเซิร์ฟเวอร์จริงของ Microsoft เมื่อเหยื่อกรอกรหัสผ่านและผ่าน MFA สำเร็จ พร็อกซีจะขโมยคุกกี้เซสชันทันที ทำให้แฮกเกอร์สามารถเข้าถึงบัญชีได้โดยไม่ต้องผ่าน MFA อีก
ฉันควรทำอย่างไรต่อไปในทางปฏิบัติ?
แคมเปญนี้หมุนเวียนใช้ชุดฟิชชิ่งอย่างน้อย 3 ตัว ได้แก่ EvilProxy, FlowerStorm และ Kali365 ซึ่งล้วนเป็นบริการ Phishing as a Service (PhaaS) ที่มีขายในตลาดมืด
cyberpress.orgHackers Use Procurement Phishing and AiTM Kits to Hijack MFA-Protected Microsoft 365 Sessions
adversis.ioYour MFA Isn't Protecting You: Inside the EvilProxy Campaigns ...
csoonline.comFlowerStorm phishing gang adopts virtual-machine ...
hackread.comFBI Warns of Kali365 Phishing Service Targeting Microsoft ...