리누스 토르발스는 AI 기반 버그 보고가 폭증하면서 리눅스 커널 보안 메일링 리스트가 “거의 관리 불가능”한 상태가 됐다고 경고했다.
여러 연구자가 같은 AI 도구로 동일한 취약점을 동시에 발견해 중복 보고가 대량 발생하고 유지관리자들의 검증 작업이 크게 늘었다.
Linux 7.1 문서는 AI 보조 버그 보고에 대해 최소 정보와 품질 기준을 명확히 하며, 실제 보안 취약점의 정의도 다시 정리했다.
What did Linus Torvalds say about AI-generated bug reports making the Linux kernel’s private security mailing list “unmanageable,” why are dAI-assisted vulnerability discovery is accelerating—but Linux maintainers say duplicate reports are overwhelming security triage.
AI 프롬프트
Create a landscape editorial hero image for this Studio Global article: What did Linus Torvalds say about AI-generated bug reports making the Linux kernel’s private security mailing list “unmanageable,” why are d. Article summary: Linus Torvalds said the Linux kernel security list had become “almost entirely unmanageable” because of a continuing flood of AI-generated reports, with “enormous duplication” as different people find and submit the same. Topic tags: general, documentation, general web, user generated. Reference image context from search candidates: Reference image 1: visual subject "We spoke about how, over the last month, AI-driven activity around Linux security and code review has "really jumped" in a way no one in the open source world saw coming. It didn't" source context "Linux kernel czar says AI bug reports aren't slop anymore" Reference image 2: visual subject "We spok
openai.com
AI 기반 코드 분석 도구는 대형 프로젝트에서 취약점을 찾는 속도를 크게 높이고 있다. 하지만 리눅스 커널 개발 커뮤니티에서는 이 기술이 새로운 문제를 만들고 있다.
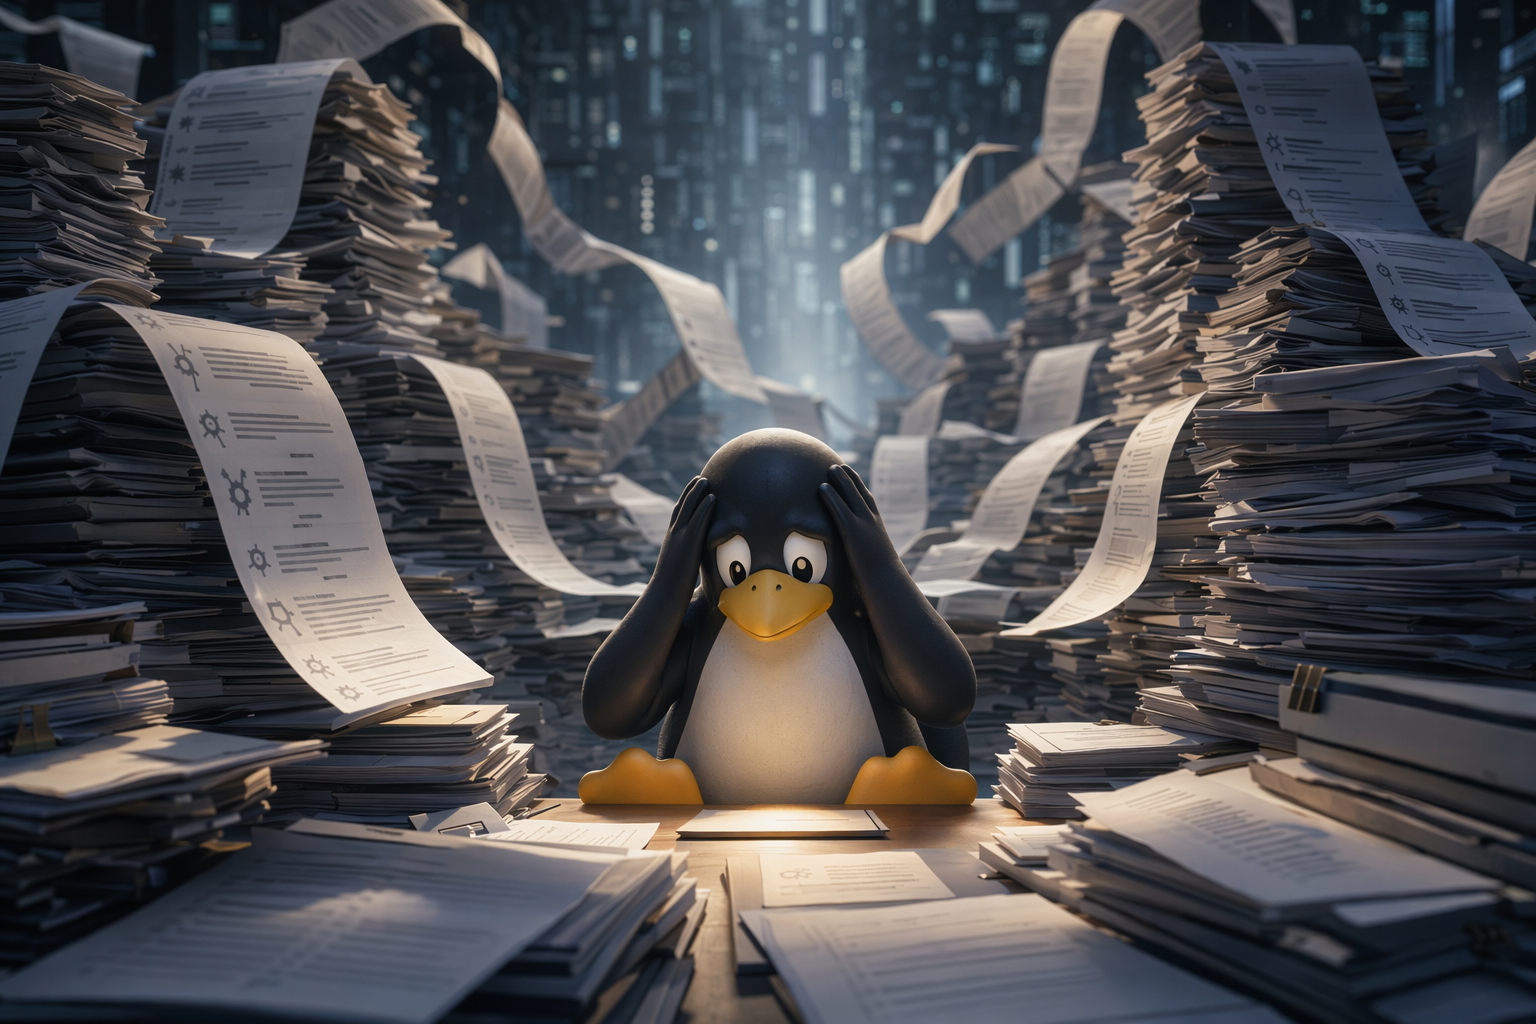
리눅스 창시자 리누스 토르발스(Linus Torvalds)는 최근 AI가 생성하거나 AI로 발견된 취약점 보고가 급증하면서 리눅스 커널의 비공개 보안 메일링 리스트가 “거의 완전히 관리 불가능한 상태”가 됐다고 경고했다. 핵심 문제는 단순히 AI가 버그를 찾는다는 점이 아니라, 여러 사람이 같은 AI 도구로 동일한 취약점을 동시에 발견하고 반복 보고한다는 것이다. 그 결과 유지관리자들은 같은 문제를 계속 검토해야 하는 상황에 놓였다.
이에 따라 커널 프로젝트는 Linux 7.1 개발 사이클에서 보안 버그 보고 방식과 AI 활용에 대한 새로운 가이드라인을 문서로 추가했다.
Studio Global AI
연구를 계속하세요
이 페이지에는 Studio Global 내에서 계속할 수 있는 소스 기반 답변이 포함되어 있습니다.
리누스 토르발스는 AI 기반 버그 보고가 폭증하면서 리눅스 커널 보안 메일링 리스트가 “거의 관리 불가능”한 상태가 됐다고 경고했다.
여러 연구자가 같은 AI 도구로 동일한 취약점을 동시에 발견해 중복 보고가 대량 발생하고 유지관리자들의 검증 작업이 크게 늘었다.
Linux 7.1 문서는 AI 보조 버그 보고에 대해 최소 정보와 품질 기준을 명확히 하며, 실제 보안 취약점의 정의도 다시 정리했다.
What did Linus Torvalds say about AI-generated bug reports making the Linux kernel’s private security mailing list “unmanageable,” why are dAI-assisted vulnerability discovery is accelerating—but Linux maintainers say duplicate reports are overwhelming security triage.
AI 프롬프트
Create a landscape editorial hero image for this Studio Global article: What did Linus Torvalds say about AI-generated bug reports making the Linux kernel’s private security mailing list “unmanageable,” why are d. Article summary: Linus Torvalds said the Linux kernel security list had become “almost entirely unmanageable” because of a continuing flood of AI-generated reports, with “enormous duplication” as different people find and submit the same. Topic tags: general, documentation, general web, user generated. Reference image context from search candidates: Reference image 1: visual subject "We spoke about how, over the last month, AI-driven activity around Linux security and code review has "really jumped" in a way no one in the open source world saw coming. It didn't" source context "Linux kernel czar says AI bug reports aren't slop anymore" Reference image 2: visual subject "We spok
openai.com
AI 기반 코드 분석 도구는 대형 프로젝트에서 취약점을 찾는 속도를 크게 높이고 있다. 하지만 리눅스 커널 개발 커뮤니티에서는 이 기술이 새로운 문제를 만들고 있다.
리눅스 창시자 리누스 토르발스(Linus Torvalds)는 최근 AI가 생성하거나 AI로 발견된 취약점 보고가 급증하면서 리눅스 커널의 비공개 보안 메일링 리스트가 “거의 완전히 관리 불가능한 상태”가 됐다고 경고했다. 핵심 문제는 단순히 AI가 버그를 찾는다는 점이 아니라, 여러 사람이 같은 AI 도구로 동일한 취약점을 동시에 발견하고 반복 보고한다는 것이다. 그 결과 유지관리자들은 같은 문제를 계속 검토해야 하는 상황에 놓였다.
이에 따라 커널 프로젝트는 Linux 7.1 개발 사이클에서 보안 버그 보고 방식과 AI 활용에 대한 새로운 가이드라인을 문서로 추가했다.
Studio Global AI
연구를 계속하세요
이 페이지에는 Studio Global 내에서 계속할 수 있는 소스 기반 답변이 포함되어 있습니다.
linux.slashdot.orgLinus Torvalds: AI-Detected Bug Reports Make Kernel Security List ...
app.daily.devLinus Torvalds says AI-powered bug hunters have made... - daily.dev
lwn.netDocumentation: security-bugs: new updates covering triage and AI