How the “Zombie Card” Attack Makes Some Expired Visa Cards Pay Again
The “Zombie Card” attack can make some expired Visa contactless cards usable for in store purchases by relaying NFC traffic through two smartphones and showing the terminal a future expiration date. The researchers found the issue in the tested Visa contactless processing path, EMV Kernel 3; comparable testing repor...
Published byEdited with GPT-5.6 LunaImages generated with GPT Image 1.5
The “Zombie Card” attack can make some expired Visa contactless cards usable for in store purchases by relaying NFC traffic through two smartphones and showing the terminal a future expiration date.
The researchers found the issue in the tested Visa contactless processing path, EMV Kernel 3; comparable testing reportedly did not reproduce the attack against Mastercard Kernel 2, American Express Kernel 4, or Disco...
Consumers should deactivate old cards with their issuer, destroy the chip and magnetic stripe, cut up the card, and monitor the associated account for unauthorized charges.
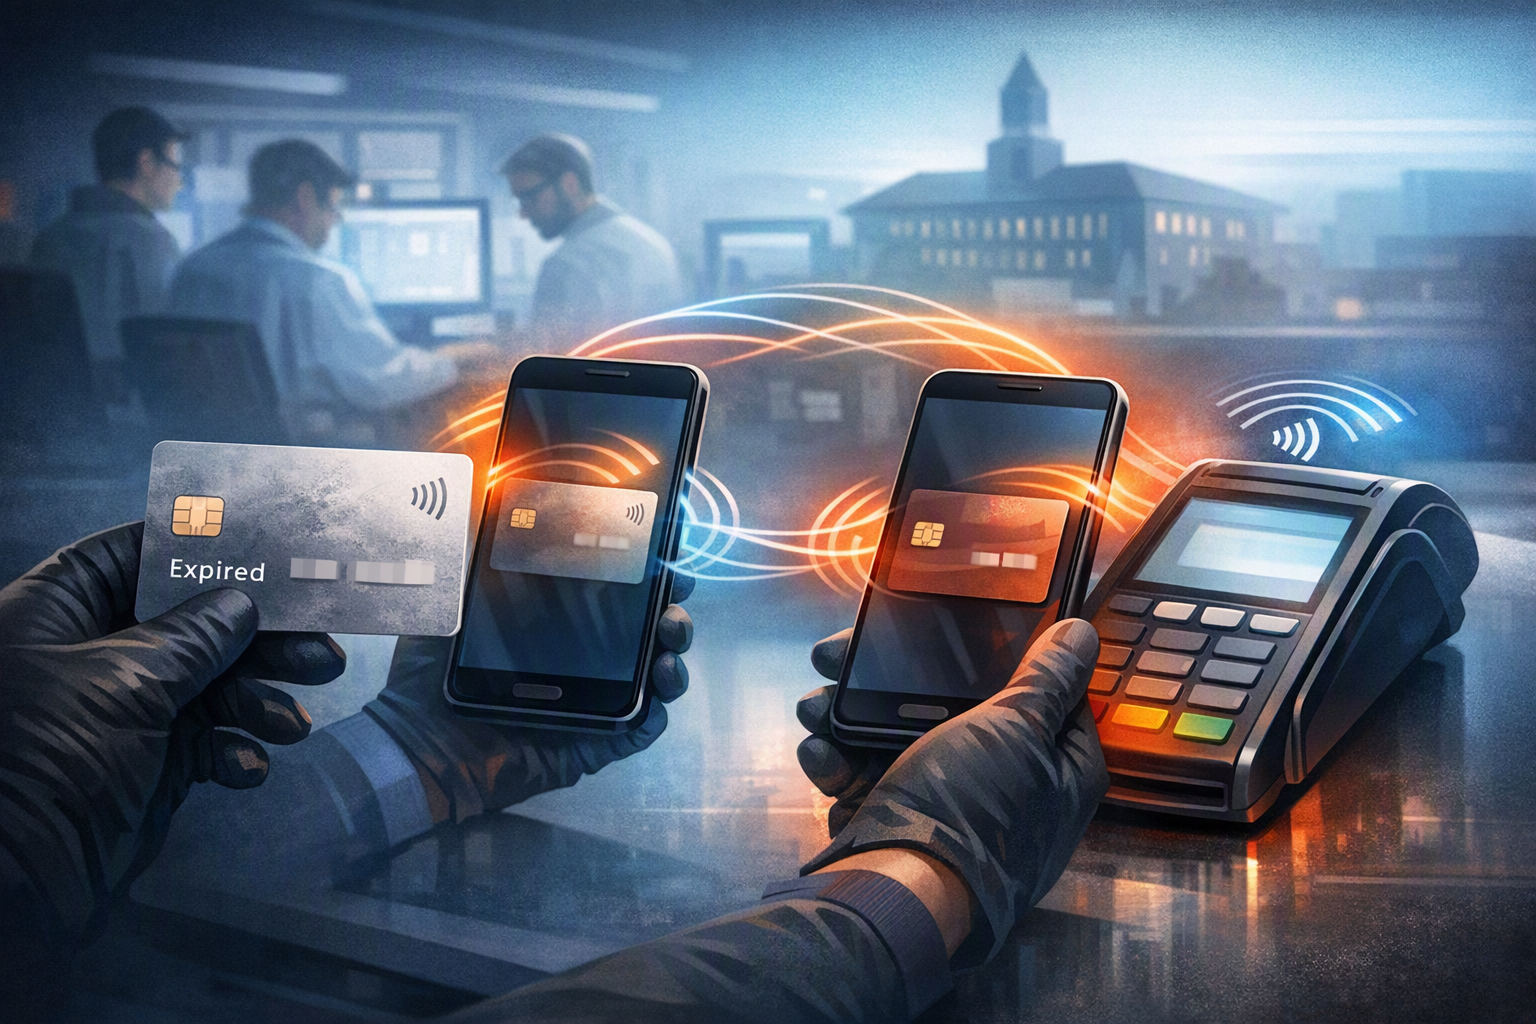
What is the “Zombie Card” NFC relay attack demonstrated by University of Massachusetts Amherst researchers at the 35th USENIX Security SympoConceptual illustration of the two-phone NFC relay described in the Zombie Card research.
AI Prompt
Create a landscape editorial hero image for this Studio Global article: What is the “Zombie Card” NFC relay attack demonstrated by University of Massachusetts Amherst researchers at the 35th USENIX Security Sympo. Article summary: “Zombie Card” is a practical NFC man-in-the-middle relay attack: two ordinary smartphones relay an expired physical contactless card to a point-of-sale terminal while altering the expiration date the terminal sees. It do. Topic tags: general, general web. Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, and topical grounding; do not copy the exact image. Avoid: logos, brand marks, copyrighted characters, real person likenesses, fake screenshots, UI text, readable text, watermarks, charts with fake numbers, clic
openai.com
A contactless card can be expired on its face yet still contain working payment credentials. Researchers at the University of Massachusetts Amherst showed how that gap can be abused in a practical NFC man-in-the-middle attack they called “Zombie Card.” Using two ordinary smartphones as a relay, an attacker can alter the expiration date presented to a point-of-sale terminal while the genuine card continues producing valid transaction data.
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "How the “Zombie Card” Attack Makes Some Expired Visa Cards Pay Again"?
The “Zombie Card” attack can make some expired Visa contactless cards usable for in store purchases by relaying NFC traffic through two smartphones and showing the terminal a future expiration date.
What are the key points to validate first?
The “Zombie Card” attack can make some expired Visa contactless cards usable for in store purchases by relaying NFC traffic through two smartphones and showing the terminal a future expiration date. The researchers found the issue in the tested Visa contactless processing path, EMV Kernel 3; comparable testing reportedly did not reproduce the attack against Mastercard Kernel 2, American Express Kernel 4, or Disco...
What should I do next in practice?
Consumers should deactivate old cards with their issuer, destroy the chip and magnetic stripe, cut up the card, and monitor the associated account for unauthorized charges.
The result is not a universal way to use every expired card. It is a payment-chain weakness that depends on the card network’s contactless implementation, the terminal, and—crucially—the issuer’s authorization checks.
What the Zombie Card attack does
The attack sits between an expired physical contactless card and a checkout terminal. One smartphone communicates with the card, while a second presents the card’s responses to the terminal; the phones relay the exchange over a network connection. During that exchange, the relay changes the expiration date that the terminal sees to a date in the future.
The researchers reported that the attacker does not need to know the expiration date of a replacement card. In the terminal-side check they described, an arbitrary future date can be enough to make the card appear current.
That does not mean the attacker has forged the card or defeated EMV cryptography. The physical card still supplies its genuine card data, signatures, and transaction cryptograms. The problem is that the expiration value used by the terminal is not adequately tied to the authenticated information later used for online authorization in the tested Visa setup.
Why Visa EMV Kernel 3 matters
EMV kernels are the payment-processing software implementations used by terminals for different card schemes. Visa, Mastercard, American Express, and Discover use distinct contactless processing paths.
The researchers’ finding concerned Visa’s EMV contactless path, identified in the supplied reporting as Kernel 3. The reported design gap allows two parts of the transaction to disagree: the terminal can receive a modified, future expiration date, while the issuer-facing transaction retains authentic card data and valid cryptographic checks.
In a more tightly bound design, changing the expiration-related value in transit would make the authenticated transaction inconsistent and cause validation to fail. The Zombie Card finding therefore illustrates an important security principle: cryptographic protection is less useful when a security-critical field is checked in one part of the payment chain but not reliably bound to the data trusted elsewhere.
Why the same technique reportedly failed on other networks
The researchers tested the approach against other contactless kernels and reported that it did not work against Mastercard Kernel 2, American Express Kernel 4, or Discover Kernel 6. The supplied reports attribute that resistance to stronger protection, validation, or cryptographic binding of the relevant expiration data.
The available evidence does not establish the exact protocol-level rule that stops the attack in each of those three kernels. It is therefore safer to state the conclusion narrowly: the demonstrated expiry-tampering method was reported as effective against the tested Visa setup, but not against the tested Mastercard, American Express, and Discover paths. It is not evidence that Visa cards are generally forgeable or that every expired Visa card will work.
What testing at five U.S. banks showed
Testing across merchants, terminals, EMV kernels, and five major U.S. banks produced mixed results. Some issuers authorized transactions containing the altered terminal-side expiration date, while others rejected them because of stronger issuer-side checks.
That variation is central to the finding. The terminal’s acceptance decision alone did not determine whether the payment completed; the issuer’s authorization logic also mattered. A bank that independently enforces card expiration, replacement, cancellation, and account lifecycle status is more likely to reject the transaction than one that relies heavily on the terminal’s expiry decision.
The supplied reporting does not provide a reliable bank-by-bank list of the five institutions, exact approval and rejection results, or verified transaction limits for each bank. Those details should not be inferred from the broader finding.
Disclosure and remediation status
The research was presented at USENIX Security 2026, and the supplied university-related reporting says that major card companies were notified before the findings were made public.
As of August 20, 2026, the supplied evidence confirms the vulnerability finding in the researchers’ evaluation but does not confirm that Visa had completed a universal kernel change, terminal update, or issuer-wide fix. It also does not establish a definitive remediation timeline for each affected bank.
That distinction matters: disclosure is not the same as completed remediation. The practical risk can vary while networks, terminal providers, acquirers, and issuers determine how to validate the relevant card-lifecycle data consistently.
Recommended defenses across the payment chain
The research points to defense in depth rather than a single fix:
Payment-kernel and card-system designers: cryptographically bind the expiration date and other lifecycle fields visible to the terminal to the authenticated transaction data. An in-transit change should invalidate the transaction.
Terminal and acquiring systems: validate expiration using authenticated information where available and reject inconsistent values instead of trusting an unprotected terminal-facing field.
Issuers: independently check expiration, replacement, cancellation, and account status during authorization rather than relying only on the terminal’s local decision.
Networks and fraud teams: look for discrepancies between terminal-provided expiry data and issuer-visible card information, while applying controls appropriate for suspicious contactless relay activity. This follows from the researchers’ finding that responsibility is split across the card, terminal, network, and issuer.
What consumers should do with expired cards
An expired card should not be thrown away intact. The guidance supplied with the research recommends demagnetizing the magnetic stripe, destroying the EMV chip, and cutting or shredding the card—including its printed numbers and letters—before discarding the pieces separately. Owners of metal cards should ask the issuer how to dispose of them safely.
Cardholders should also monitor the associated account, including after a card has been closed, and report unauthorized charges promptly. The attack requires access to the physical card or sustained proximity to it, so securely destroying an old card reduces the opportunity for abuse.
pasqualepillitteri.itCartes bancaires expirées qui repaient : la faille sans contact qui ...
xenospectrum.comAttack Revives Expired Credit Cards Using Two Smartphones | XenoSpectrum
theregister.comExpired credit cards revived by researchers to make ...
khwarizmilab.github.ioZombie Cards Back Online: Expired Card Attack - Khwarizmi Lab
cybersecuritynews.comNew “Zombie Card” Flaw Lets Expired Visa Cards Make Contactless Payments