Delta Flight 591: How a Fake Wi-Fi Hotspot Sparked a Mid-Air Cyber Incident and FBI Investigation
On August 10, 2026, a passenger on Delta Flight 591 from Las Vegas to Atlanta allegedly jammed the legitimate in flight Wi Fi and broadcast a rogue 'evil twin' hotspot named 'Delta WiFi Fast' to phish fellow travelers.
Published byEdited with DeepSeek-V4-FlashImages generated with GPT Image 1.5
On August 10, 2026, a passenger on Delta Flight 591 from Las Vegas to Atlanta allegedly jammed the legitimate in flight Wi Fi and broadcast a rogue 'evil twin' hotspot named 'Delta WiFi Fast' to phish fellow travelers.
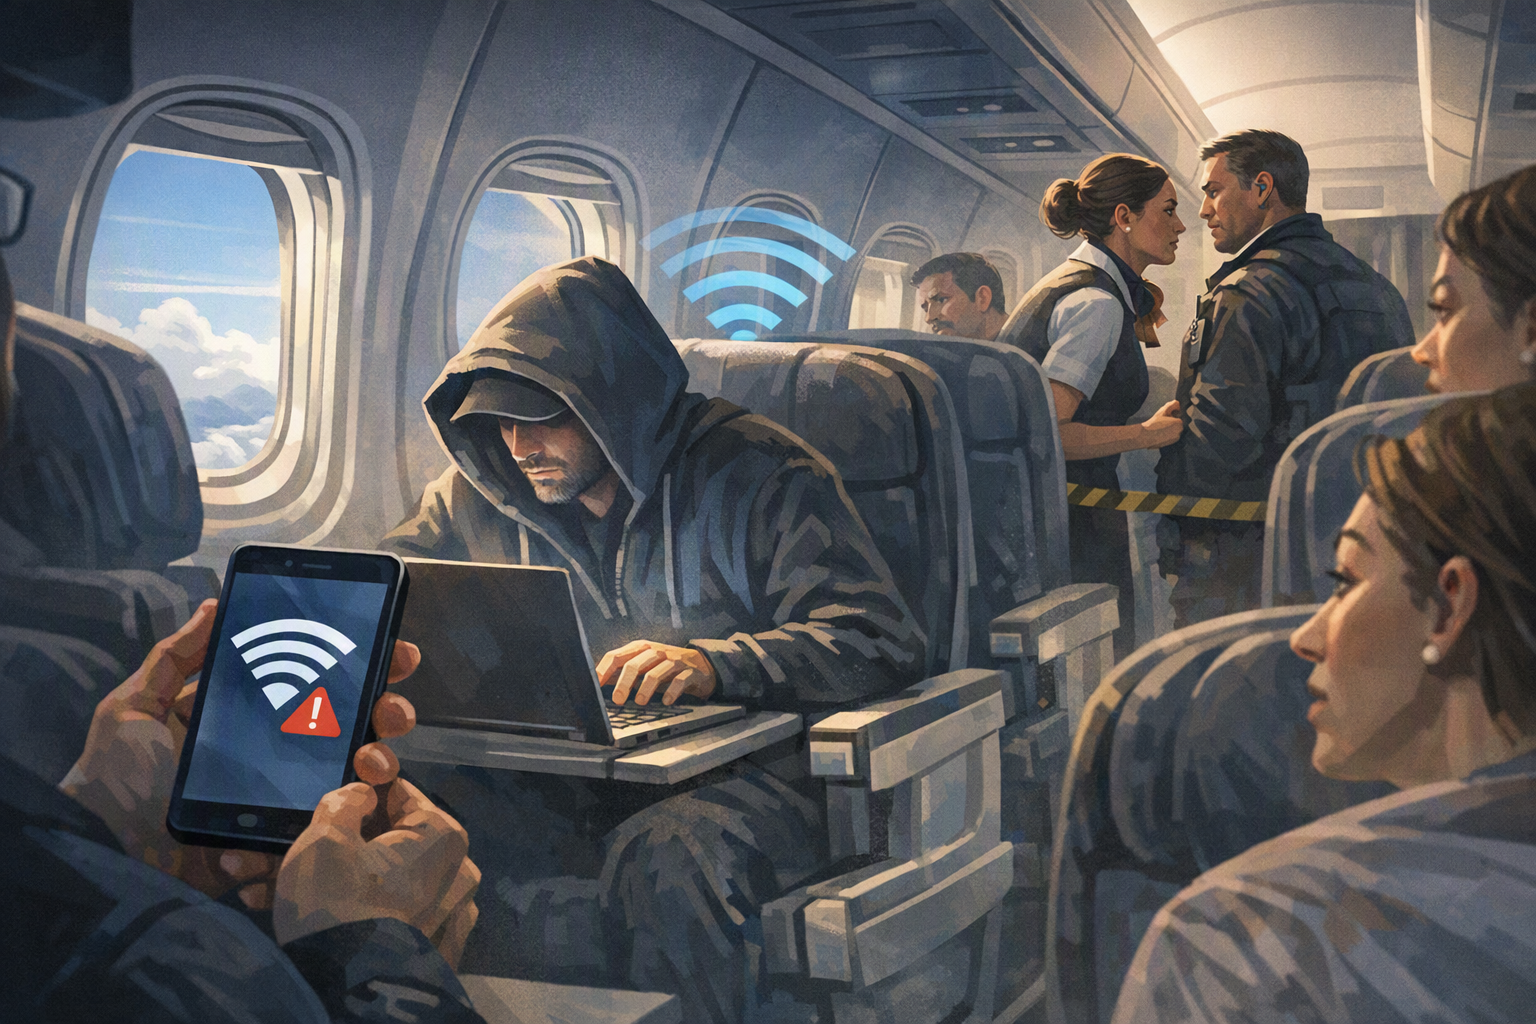
What happened on a Delta flight from Las Vegas to Atlanta after an unidentified passenger allegedly set up a fake Wi-Fi network mid-flight,Conceptual illustration of an in-flight cyber incident. Delta Flight 591 experienced an 'evil twin' Wi-Fi attack mid-flight on August 10, 2026.
AI Prompt
Create a landscape editorial hero image for this Studio Global article: What happened on a Delta flight from Las Vegas to Atlanta after an unidentified passenger allegedly set up a fake Wi-Fi network mid-flight,. Article summary: Here is a comprehensive summary of what happened, based on multiple news and security sources from August 11–12, 2026.. Topic tags: general, general web. Style: premium digital editorial illustration, source-backed research mood, clean composition, high detail, modern web publication hero. Use reference image context only for broad subject, composition, and topical grounding; do not copy the exact image. Avoid: logos, brand marks, copyrighted characters, real person likenesses, fake screenshots, UI text, readable text, watermarks, charts with fake numbers, clickbait thumbnails, icons, and tiny thumbnail layouts. Make it useful as an illustrative visual, not as f
openai.com
On Monday, August 10, 2026, a routine Delta flight from Las Vegas to Atlanta turned into a cybersecurity incident that triggered a federal investigation. About an hour after takeoff, a passenger on Delta Flight 591 — a Boeing 757 carrying 199 passengers and six crew members — allegedly jammed the aircraft's legitimate in-flight Wi-Fi and set up a fake hotspot designed to steal personal data from other passengers .
The incident occurred on a flight carrying attendees returning home from DEF CON 34, the world's largest hacking conference, which had wrapped up the day before in Las Vegas . While the airline confirmed that no aircraft operating systems or avionics were ever affected, the event prompted an immediate law enforcement response and raised urgent questions about the security of in-flight connectivity.
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "Delta Flight 591: How a Fake Wi-Fi Hotspot Sparked a Mid-Air Cyber Incident and FBI Investigation"?
On August 10, 2026, a passenger on Delta Flight 591 from Las Vegas to Atlanta allegedly jammed the legitimate in flight Wi Fi and broadcast a rogue 'evil twin' hotspot named 'Delta WiFi Fast' to phish fellow travelers.
The unidentified passenger used a portable device to jam the plane's official Wi-Fi signal and then broadcast a rogue network named 'Delta WiFi Fast' — designed to look identical to Delta's legitimate login page . This technique is known as an 'evil twin' attack: a lookalike Wi-Fi network that tricks nearby devices into connecting to a fake login page, where the attacker can harvest whatever credentials passengers enter .
According to a person who claims to have been present when the plane landed, the fake hotspot served up a phishing landing page specifically designed to capture passengers' personal credentials and Google login data. The attacker's goal was likely credential theft and personal data collection from unsuspecting travelers .
Crew Response and Pilot Communications
When the crew discovered the unauthorized network, they acted quickly. The pilots used the Aircraft Communications Addressing and Reporting System (ACARS) — a digital messaging system used for non-voice communication between aircraft and ground stations — to alert Delta's corporate security. The message read: "HEY ALERT CORP SECURITY WE HAVE A PAX [passenger] ON THAT HAS CREATED A SCAM WIFI CALLED DELTA WIFI F…" .
Seventeen minutes later, the crew sent a follow-up: "NO INFO AS OF NOW," indicating they were still gathering information. They reported that several passengers had attended a cybersecurity conference in Las Vegas and "were able to jam our Wi-Fi and broadcast…" . The pilots also directly alerted air traffic control about the unauthorized network .
As a precaution, the cabin crew disabled the aircraft's legitimate in-flight Wi-Fi system for approximately 30 minutes.
Airline Response and Safety Impact
Delta Air Lines confirmed that the safety of flight was never in question. The company stated that no aircraft operating systems or avionics were affected — the incident was strictly limited to the passenger internet network . Delta spokesperson Morgan Durrant told TechCrunch: "[The] safety of flight was never in question and no aircraft operating systems were affected," adding that the in-flight network itself was not compromised .
Once the aircraft landed at Hartsfield-Jackson Atlanta International Airport, authorities boarded the plane and interviewed passengers . Delta released a statement saying, "We are fully investigating to gather a complete set of facts, which will take time. We will partner with federal law enforcement and aviation regulators to ensure the incident is thoroughly investigated" .
Tools Likely Used in the Attack
Security researchers and reports indicate the attacker likely used a combination of two techniques: a Wi-Fi 'deauthentication' attack (deauth attack) to forcibly disconnect passengers from the legitimate network, and a portable 'evil twin' access point to broadcast the fake hotspot .
Common tools that could have been used include:
Wi-Fi Pineapple — a popular penetration-testing device that can perform deauth attacks and broadcast fake SSIDs
Laptop running software such as aircrack-ng, bettercap, or hostapd with a wireless card capable of monitor mode
Raspberry Pi configured as a rogue access point
Federal Agencies Involved
As of August 12, 2026, three entities are actively investigating:
FBI Atlanta — reviewing the incident and working with Delta
Federal Aviation Administration (FAA) — involved in the investigation
Delta's corporate security — conducting its own internal probe
No arrests have been announced, and the passenger(s) responsible have not been publicly identified. The investigation is ongoing.
Key Takeaways
No aircraft systems were affected. The incident was limited to the passenger Wi-Fi network and did not touch any flight-critical avionics .
The crew acted appropriately. By shutting down the Wi-Fi and alerting corporate security and air traffic control, they contained the threat while maintaining flight safety .
This was a credential-phishing attempt, not a flight hack. The attacker's goal was to capture login data from passengers who connected to the fake network .
Federal investigations are underway. The FBI, FAA, and Delta's security team are working to identify the responsible party .
tomshardware.com
Passenger returning from DEF CON 34 spoofs Delta Wi-Fi network ...