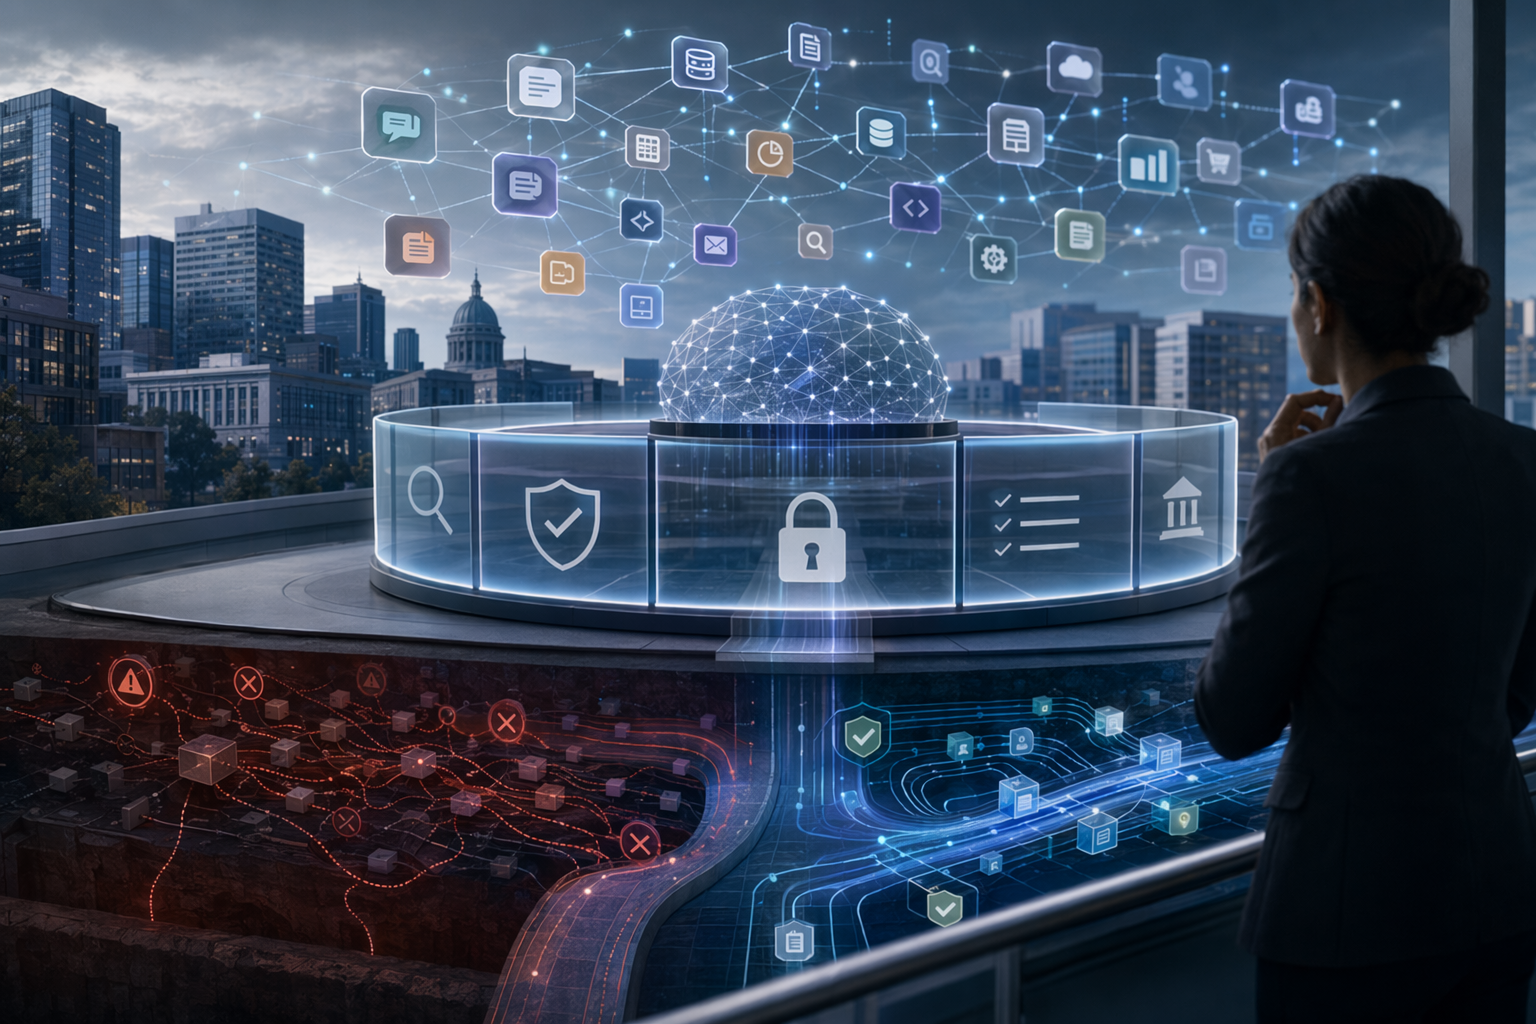
How Giskard Guards Aims to Secure Enterprise AI Agents
Giskard Guards is designed as a runtime security and governance layer for enterprise AI agents, monitoring the full execution chain and enforcing policy‑as‑code rules so organizations can safely deploy agents in regul... Traditional moderation filters only check prompts or outputs, but modern AI agents retrieve data...
Published byEdited with GPT-5.5Images generated with GPT Image 2
Giskard Guards is designed as a runtime security and governance layer for enterprise AI agents, monitoring the full execution chain and enforcing policy‑as‑code rules so organizations can safely deploy agents in regul...
Traditional moderation filters only check prompts or outputs, but modern AI agents retrieve data, call tools, and execute multi‑step actions—creating risks such as hallucinated actions, prompt injection, and unsafe to...
By combining multiple detectors, real‑time monitoring, and EU AI Act–aligned governance controls, Giskard aims to help sectors like banking, insurance, and healthcare run AI agents while maintaining compliance and sec...
How is the French startup Giskard addressing the growing security and governance risks of enterprise AI agents with its Giskard Guards platfEnterprise AI agents introduce new security and governance challenges as they interact with tools, data, and automated workflows.
AI Prompt
Create a landscape editorial hero image for this Studio Global article: How is the French startup Giskard addressing the growing security and governance risks of enterprise AI agents with its Giskard Guards platf. Article summary: Giskard is positioning Giskard Guards as a runtime security and governance layer for enterprise AI agents: instead of only filtering a user prompt or final model output, it evaluates the agent’s broader execution context. Topic tags: general, academic, general web, government. Reference image context from search candidates: Reference image 1: visual subject "The scale of the problem AI agents are proliferating across enterprise environments faster than security teams can track 10,000+ Apps on average in a single enterprise environment" source context "Enterprise AI Agent Security and Governance: Managing Risks in 2026 | PPTX" Reference image 2: visual subject "
openai.com
AI agents are quickly moving from experiments to real enterprise workflows. They retrieve documents, interact with APIs, and take multi‑step actions across business systems. That shift has introduced new risks—prompt injection, hallucinated actions, data leaks, and unsafe tool usage—that traditional AI moderation systems were never designed to handle.
French startup Giskard is addressing this gap with Giskard Guards, a runtime security and governance platform built specifically for enterprise AI agents. Instead of treating safety as a simple content filter, the platform attempts to secure the entire execution flow of an AI agent and enforce organizational policies in real time.
The Security Gap in Modern AI Agents
Early AI safety systems focused on filtering user prompts and generated text. That approach worked when language models were mostly chat interfaces producing static outputs.
Modern enterprise agents behave very differently. They can:
retrieve external documents or internal company data
call APIs and automation tools
execute multi‑step reasoning or workflows
interact with sensitive operational systems
Because of this expanded capability, the main risk has shifted from “bad content” to “bad behavior.” Agents may hallucinate facts, follow malicious instructions embedded in retrieved documents, leak sensitive information, or perform unintended actions through connected tools. These failures can disrupt business processes or expose confidential data if they occur inside production workflows.
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "How Giskard Guards Aims to Secure Enterprise AI Agents"?
Giskard Guards is designed as a runtime security and governance layer for enterprise AI agents, monitoring the full execution chain and enforcing policy‑as‑code rules so organizations can safely deploy agents in regul...
What are the key points to validate first?
Giskard Guards is designed as a runtime security and governance layer for enterprise AI agents, monitoring the full execution chain and enforcing policy‑as‑code rules so organizations can safely deploy agents in regul... Traditional moderation filters only check prompts or outputs, but modern AI agents retrieve data, call tools, and execute multi‑step actions—creating risks such as hallucinated actions, prompt injection, and unsafe to...
What should I do next in practice?
By combining multiple detectors, real‑time monitoring, and EU AI Act–aligned governance controls, Giskard aims to help sectors like banking, insurance, and healthcare run AI agents while maintaining compliance and sec...
Traditional guardrails—often implemented as simple keyword or classification filters—struggle in these environments. They frequently lack operational context, which means they may block legitimate requests while missing complex attacks such as prompt injection across multiple workflow steps. In some cases, generic guardrails can produce high false‑positive rates while still failing to detect multi‑step exploitation.
Giskard Guards: A Runtime Safety Layer for AI Agents
Giskard positions Guards as a security layer that sits between AI agents and the systems they interact with.
Instead of inspecting only the prompt or final response, the platform analyzes the broader context of an agent’s execution. This includes prompts, intermediate steps, tool calls, and outputs. The goal is to identify risky behavior before it reaches production systems.
Key elements of the approach include:
Context‑aware guardrails
The system evaluates the intent and context of interactions rather than relying solely on keyword matching. This allows guardrails to consider how a request relates to the agent’s task, connected tools, and available data.
Multiple detection layers
Guards uses several detectors simultaneously—such as checks for jailbreak attempts, prompt injection, sensitive data exposure, or policy violations. If suspicious behavior is detected, the system can allow, monitor, or block the interaction.
Execution‑chain monitoring
Rather than focusing only on inputs and outputs, the platform inspects the entire chain of agent actions. This is important because attacks can emerge from intermediate steps, such as malicious instructions embedded in retrieved documents or risky tool invocations.
Policy‑as‑Code Governance for AI Systems
A central design idea behind the platform is policy‑as‑code.
Organizations often have governance rules—privacy policies, compliance requirements, or internal safety guidelines—that must be enforced when AI systems interact with data or operational tools. Instead of relying on prompts or manual reviews, policy‑as‑code converts those rules into machine‑enforceable controls.
Research on agent governance highlights the importance of translating natural‑language policies and technical documentation into runtime guardrails that monitor and restrict AI behavior. These frameworks compile policy rules into lightweight classifiers or enforcement layers capable of monitoring agent activity in real time.
With this model, enterprises can define rules such as:
blocking disclosure of medical or financial data
requiring human review before high‑impact decisions
restricting which tools an agent can call
logging actions for compliance and auditing
Because these rules are versioned and programmable, they can evolve alongside rapidly changing AI systems.
Aligning With the EU AI Act
Another major motivation for governance‑driven guardrails is regulatory compliance.
The EU AI Act introduces a risk‑based regulatory framework that imposes stricter requirements on “high‑risk” AI systems—particularly those affecting health, safety, employment, or access to essential services. These systems must meet obligations related to risk management, documentation, transparency, logging, robustness, and human oversight.
Platforms like Giskard Guards attempt to help organizations meet these obligations by:
monitoring system behavior and maintaining logs
enforcing policy controls during runtime
enabling oversight and auditing of automated decisions
Such mechanisms can support requirements such as human oversight and technical robustness for high‑risk AI systems.
Why Regulated Industries Care Most
The need for agent governance is particularly strong in sectors with strict regulatory and safety requirements.
Banking and insurance organizations may deploy AI agents for tasks such as underwriting analysis, fraud detection, claims processing, and customer support. These workflows involve sensitive financial data and regulatory obligations, making it critical to prevent unauthorized actions or data exposure.
Healthcare presents even higher stakes. AI agents may summarize clinical records, retrieve patient information, or assist with triage and documentation. Guardrails must ensure that confidential medical data is protected and that automated suggestions do not bypass required human oversight.
Because of these constraints, enterprises often require security controls that operate at the infrastructure level rather than relying solely on model prompts or guidelines.
Europe’s Push for Sovereign AI Infrastructure
Giskard also positions Guards as part of a broader European “sovereign AI” approach.
The platform is designed to support on‑premise or controlled deployments so regulated organizations can keep sensitive data, telemetry, and policy enforcement within their own infrastructure. This approach aims to reduce reliance on external moderation APIs and align with European data governance priorities.
For companies operating under EU regulatory frameworks such as GDPR and the AI Act, the ability to control where AI safety and monitoring infrastructure runs can be a significant factor in deployment decisions.
The Bigger Shift: Securing AI Behavior, Not Just Content
The rise of AI agents is changing how safety systems must operate. Guardrails that only analyze prompts or generated text cannot capture the complexity of systems that plan tasks, access data, and interact with tools.
Giskard’s approach reflects a broader shift in AI security: monitoring the behavior of AI agents throughout their entire workflow and enforcing governance rules in real time.
Whether platforms like Guards can reliably prevent complex failures across large‑scale enterprise deployments remains an open question. But the concept of context‑aware, policy‑driven runtime security is increasingly seen as a necessary layer as AI agents move deeper into business‑critical systems.
AI Security Resources | LLM Testing & Red Teaming - Giskard