SAP’s 2026 API policy: what changes for third-party AI agents and ERP data
SAP’s April 2026 update narrows supported API use toward published, documented APIs and SAP endorsed pathways; third party AI agents that plan and execute multi step API calls may need approved routes.[1][5][10] The highest risk scenarios are undocumented interfaces, bulk extraction or replication of SAP data, and e...
Published byEdited with GPT-5.5Images generated with GPT Image 2
SAP’s April 2026 update narrows supported API use toward published, documented APIs and SAP endorsed pathways; third party AI agents that plan and execute multi step API calls may need approved routes.[1][5][10]
The highest risk scenarios are undocumented interfaces, bulk extraction or replication of SAP data, and external orchestration layers that directly read or write core ERP workflows.[7][9][13]
User groups including DSAG have criticised the uncertainty, while lock in concerns now depend heavily on how SAP maintains its API catalogues, endorsed pathways and approval mechanisms.[2][10][11]
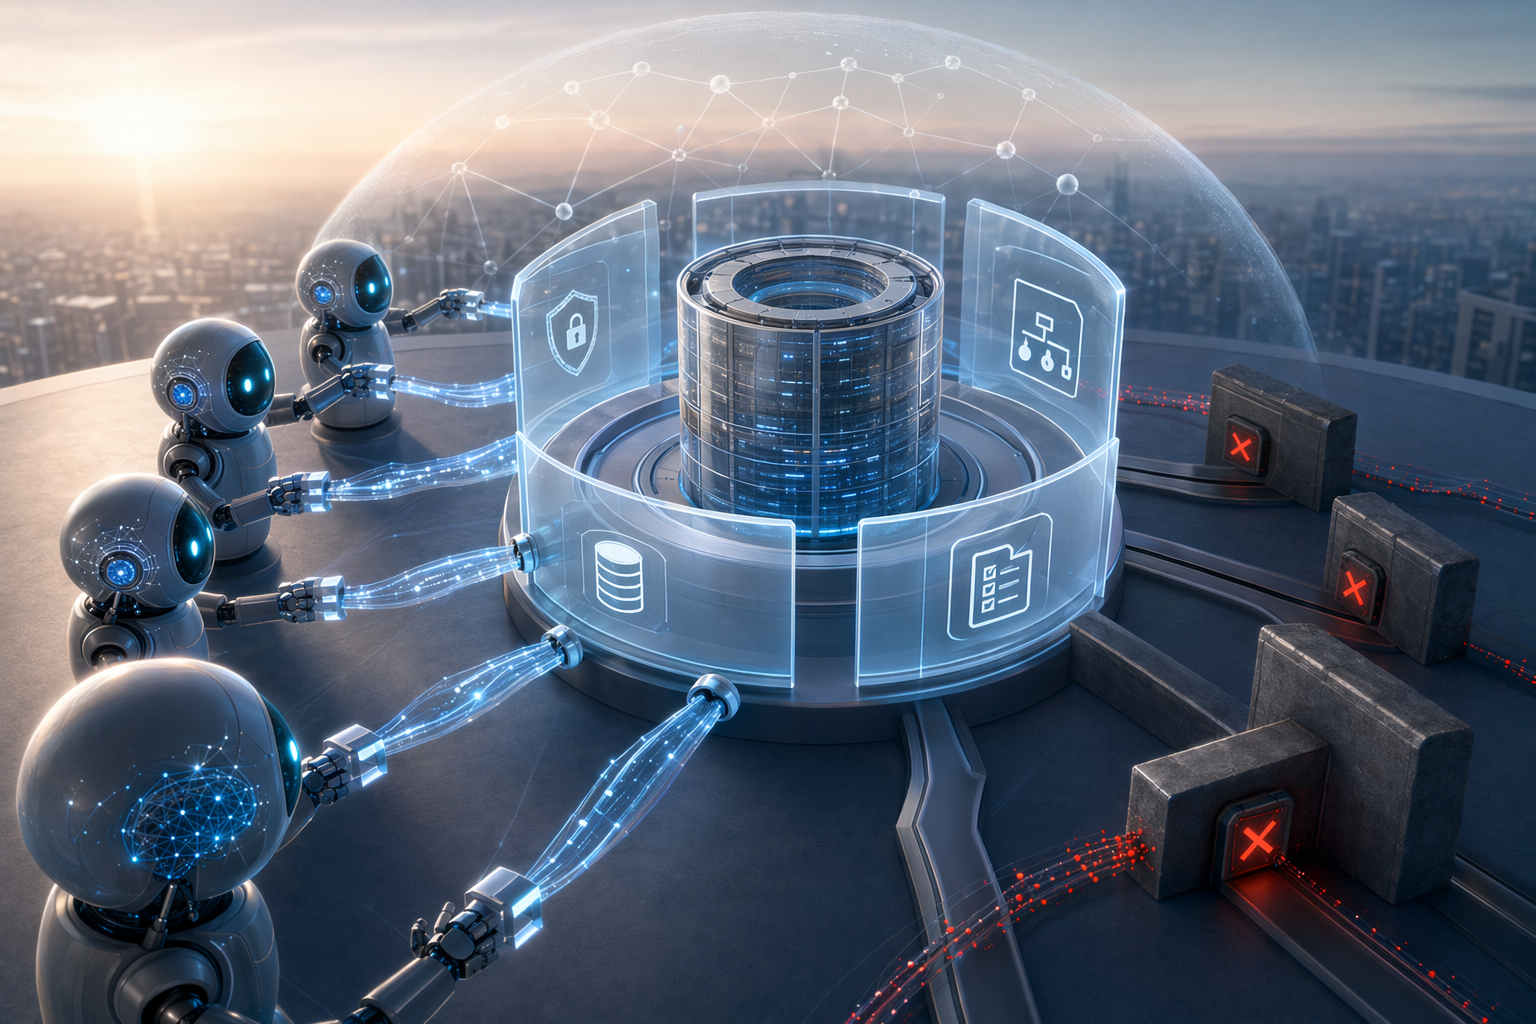
SAP 2026 API 新政策:第三方 AI Agent 存取 ERP 數據的新邊界AI 生成示意圖:SAP 新 API 政策把第三方 AI agent 的 ERP 數據存取推向更受控的官方路徑。
AI Prompt
Create a landscape editorial hero image for this Studio Global article: SAP 2026 API 新政策:第三方 AI Agent 存取 ERP 數據的新邊界. Article summary: SAP 2026 年 4 月 API 政策將會規劃、選擇或執行多步 API calls 的第三方 AI agent,限制在 SAP 認可架構、數據服務或指定路徑之內;這不是全面禁用第三方整合,但會增加合規審查、重構和鎖定風險。[1][10]. Topic tags: sap, erp, ai agents, enterprise ai, api. Reference image context from search candidates: Reference image 1: visual subject "*这是2026年4月的科技雷达:一份每周分析,解读和将其转化为决策的信号,供企业和 IT 领导者参考。这不是新闻摘要,而是应用于商业的智能。五个关键领域,十五个具体信号,以及三个应该在本周的议程中做出改变的结论。.*. ## SAP 新闻 — 2026 年 4 月技术雷达. ### [女高音] SAP S/4HANA 2025:Joule 及其分析 AI 和" source context "2026年4月科技雷达:SAP、代理AI与农业科技" Reference image 2: visual subject "*这是2026年4月的科技雷达:一份每周分析,解读和将其转化为决策的信号,供企业和 IT 领导者参考。这不是新闻摘要,而是应用于商业的智能。五个关键领域,十五个具体信号,以及三个应该在本周的议程中做出改变的结论。.*. ## SAP 新闻 — 2026 年 4 月技术雷达. ### [女高音] SAP S/4HANA 2025:Joule 及其分析 AI 和" source context "2026年4月科技雷达:SAP、代理AI与农业科技" Style: premium digital
openai.com
SAP’s April 2026 API policy update is best read as a new perimeter around how non-SAP systems reach core ERP data and workflows — not as a simple ban on every third-party integration. For IT leaders, the practical question is no longer only whether an interface can be called, but whether it is a published, documented API used within a SAP-endorsed architecture, data service or service-specific pathway.
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "SAP’s 2026 API policy: what changes for third-party AI agents and ERP data"?
SAP’s April 2026 update narrows supported API use toward published, documented APIs and SAP endorsed pathways; third party AI agents that plan and execute multi step API calls may need approved routes.[1][5][10]
What are the key points to validate first?
SAP’s April 2026 update narrows supported API use toward published, documented APIs and SAP endorsed pathways; third party AI agents that plan and execute multi step API calls may need approved routes.[1][5][10] The highest risk scenarios are undocumented interfaces, bulk extraction or replication of SAP data, and external orchestration layers that directly read or write core ERP workflows.[7][9][13]
What should I do next in practice?
User groups including DSAG have criticised the uncertainty, while lock in concerns now depend heavily on how SAP maintains its API catalogues, endorsed pathways and approval mechanisms.[2][10][11]
That shift lands directly on AI agents, data replication jobs, integration platforms and in-house automations that were designed to reach SAP as if every callable interface were equally supported.
What actually changed
SAP has made the API boundary more formal. CIO reported SAP’s position that only interfaces listed in SAP Business Accelerator Hub — SAP’s public catalogue for APIs and integration content — or in the relevant product documentation are considered published APIs. The Register also reported that the new policy requires API use to remain within SAP-endorsed architectures, data services, or service-specific pathways.
The policy also sets out API controls that can include functional and technical rate limits, quotas, deprecation schedules, data ingress and egress quotas, limits and preconditions for bulk extraction or replication, and other security or technical requirements.
That matters because many enterprise landscapes have grown around older, custom or undocumented touchpoints. SAPinsider notes that undocumented APIs are still widely used, but now fall outside support boundaries, increasing long-term integration and operational risk.
In plain English, the test has changed from: can our developers make this SAP call work? to: is this call published, supported, used for an allowed purpose and routed through an endorsed pattern?
Why AI agents are especially sensitive
The most debated part is the AI clause. Reports from Fivetran and The Register both highlight policy language that prohibits API use for interaction or integration with semi-autonomous or generative AI systems that plan, select or execute sequences of API calls, except through SAP-controlled or SAP-endorsed routes.
That language targets agentic behaviour. A conventional integration might make one predictable API call when a fixed event occurs. An AI agent may decide its next step dynamically: check a supplier, compare inventory, inspect purchase orders, generate a recommendation and then trigger an approval or update a record. If the system is selecting and chaining SAP API calls as part of a multi-step plan, it can fall into the category that now needs careful policy review.
The same restriction also covers scraping, harvesting, and systematic or large-scale data extraction or replication. So the issue is not limited to AI agents that write back into SAP. Read-heavy designs — for example, feeding an external lakehouse, AI platform or orchestration layer with large volumes of SAP data — also need to be rechecked against SAP’s data ingress and egress quotas, bulk extraction conditions and approved pathways.
What it means for customer innovation
The policy does not mean every AI proof of concept must stop. It does mean an SAP-connected AI proof of concept now looks much more like a governed integration project. Before a team lets an external agent touch ERP data, it needs to confirm which APIs are being used, whether they appear in SAP Business Accelerator Hub or product documentation, whether the architecture is endorsed, whether usage triggers quotas, and whether the agent is independently planning multi-step API calls.
That adds friction for innovation teams, systems integrators and software vendors. Experiments around automated reconciliation, procurement support, inventory analysis or service workflow automation may still be possible, but they need a clearer paper trail: API inventory, identity and permission design, usage estimates, data-flow review and compliance sign-off.
ERP Today describes the shift as more than a technical integration issue: it turns API access into a broader ERP architecture concern, because existing integrations may depend on interfaces that are not formally documented while new AI applications need controlled access to enterprise data and transactional workflows.
Uncertainty is part of the problem. The Register reported that the German-speaking SAP User Group, DSAG, criticised the policy for creating uncertainty; the same report noted criticism that SAP’s approved interface list may not be well managed or kept up to date.
Data control: access is the real battleground
The argument is not only about who owns customer data. For SAP customers, the sharper question is whether they can use their preferred AI platform, data stack or automation tool to access SAP data and transaction flows directly, continuously and in real time.
The Register framed the concern as third-party AI tools potentially being locked out of customers’ SAP data, while ERP Today placed the issue in the wider architecture of ERP integration, data replication and AI access.
For any organisation synchronising SAP data into an external lakehouse, AI platform, workflow engine or third-party automation system, the checklist now has to include data ingress and egress quotas, bulk extraction or replication prerequisites, the scope of published APIs, and whether SAP requires an endorsed route for that use case.
There is a governance upside: tighter controls can make performance, security, audit and data-movement rules more explicit. The trade-off is that cross-platform AI architectures may have less room to operate independently, especially when they need high-volume or frequent access to SAP transaction data.
Vendor lock-in risk rises — but it is not automatic
The lock-in concern is straightforward. If a third-party AI agent cannot freely interact with SAP APIs, customers may become more dependent on SAP-endorsed architectures, SAP data services or integration paths that SAP explicitly permits. The Register has already described the AI clause as provoking lock-in concerns because it may keep some third-party AI tools away from customers’ SAP data.
DSAG’s reaction shows this is not just a developer complaint. E3 Magazine reported that the user group viewed SAP’s strict restrictions on undocumented uses, systematic mass data extraction and interaction with autonomous generative AI systems from third-party providers as unacceptable.
Still, lock-in is not the only possible outcome. Much depends on SAP’s execution: whether endorsed pathways are clearly defined, whether the published API catalogue is complete and current, whether exceptions or approvals are auditable, and whether third-party vendors can continue to innovate under rules that are predictable. Critics have already questioned the management and timeliness of approved interface lists, which is exactly where customers should focus their due diligence.
Five practical steps for SAP customers
Inventory every SAP integration. Classify each connection as a published API, product-documented API, undocumented interface, bulk extraction job, real-time read/write flow, integration middleware call, RPA script or external workflow/agent call.
Flag agentic AI use cases early. Any system in which a model or agent can plan, choose or execute multiple SAP API calls should go through a specific policy and architecture review before scaling beyond experimentation.
Audit extraction and replication. Large-scale extraction, replication, scraping and harvesting are explicitly in the risk zone. Existing data lake, lakehouse, BI, AI training and synchronisation architectures should be checked against quotas, prerequisites and allowed pathways.
Get written confirmation for edge cases. For agentic AI, automated transaction updates, cross-system orchestration and bulk data export, do not rely only on informal interpretations. DSAG’s criticism of uncertainty shows why documented boundaries matter.
Preserve architecture choice. Even if the final design uses SAP-endorsed routes, keep AI orchestration, data governance, permissions, audit logging and business rules as modular as possible. That makes it easier to change tools or pathways later if the policy, API catalogue or commercial model changes.
Bottom line
SAP’s 2026 API policy does not mean AI cannot use SAP. It means third-party AI agents can no longer assume they may freely orchestrate SAP APIs, especially when they plan and execute multi-step calls or move data at scale. The policy raises the bar for governance, quotas and supported access, while also increasing compliance work, slowing some experiments and sharpening vendor lock-in concerns.
The near-term response is practical: map your integrations, identify agentic AI flows, confirm which SAP-endorsed pathways apply, and design new architectures with enough modularity to preserve cross-platform choice.
theregister.com
SAP user group slams 'uncertainty' in ERP giant's API policy
sapinsider.orgSAP API Policy Update Raises Concerns for Developers and Partners
cio.comSAP's new API policy restricts AI access, draws customer criticism
theregister.comAI clause in new SAP API policy provokes lock-in concern
erp.todaySAP API Policy Raises New Questions About ERP Integration and AI ...