What are AI agents, and are they worth using in 2025?
AI agents are not just chatbots. NIST describes systems that can perceive environments, use tools and take actions beyond text output, while IBM highlights tool and API use for more complex goals.[1][5] In 2025, the sensible approach is a controlled pilot: MIT’s 2025 AI Agent Index found that only 9 of 30 prominent...
Published byEdited with GPT-5.5Images generated with GPT Image 2
AI agents are not just chatbots. NIST describes systems that can perceive environments, use tools and take actions beyond text output, while IBM highlights tool and API use for more complex goals.[1][5]
In 2025, the sensible approach is a controlled pilot: MIT’s 2025 AI Agent Index found that only 9 of 30 prominent agents had documented sandboxing or VM isolation, and only 4 of 13 high autonomy agents disclosed any a...
Enterprise interest is real, but ROI is not automatic. Microsoft says more than 230,000 organizations, including 90% of the Fortune 500, have used Copilot Studio to build AI agents and automations, but each workflow s...
AI Agent/Agentic AI 係乜?2025 年值唔值得用?AI agent 的關鍵,不只是聊天,而是把 AI 模型連接到工具、API 和受控流程。
AI Prompt
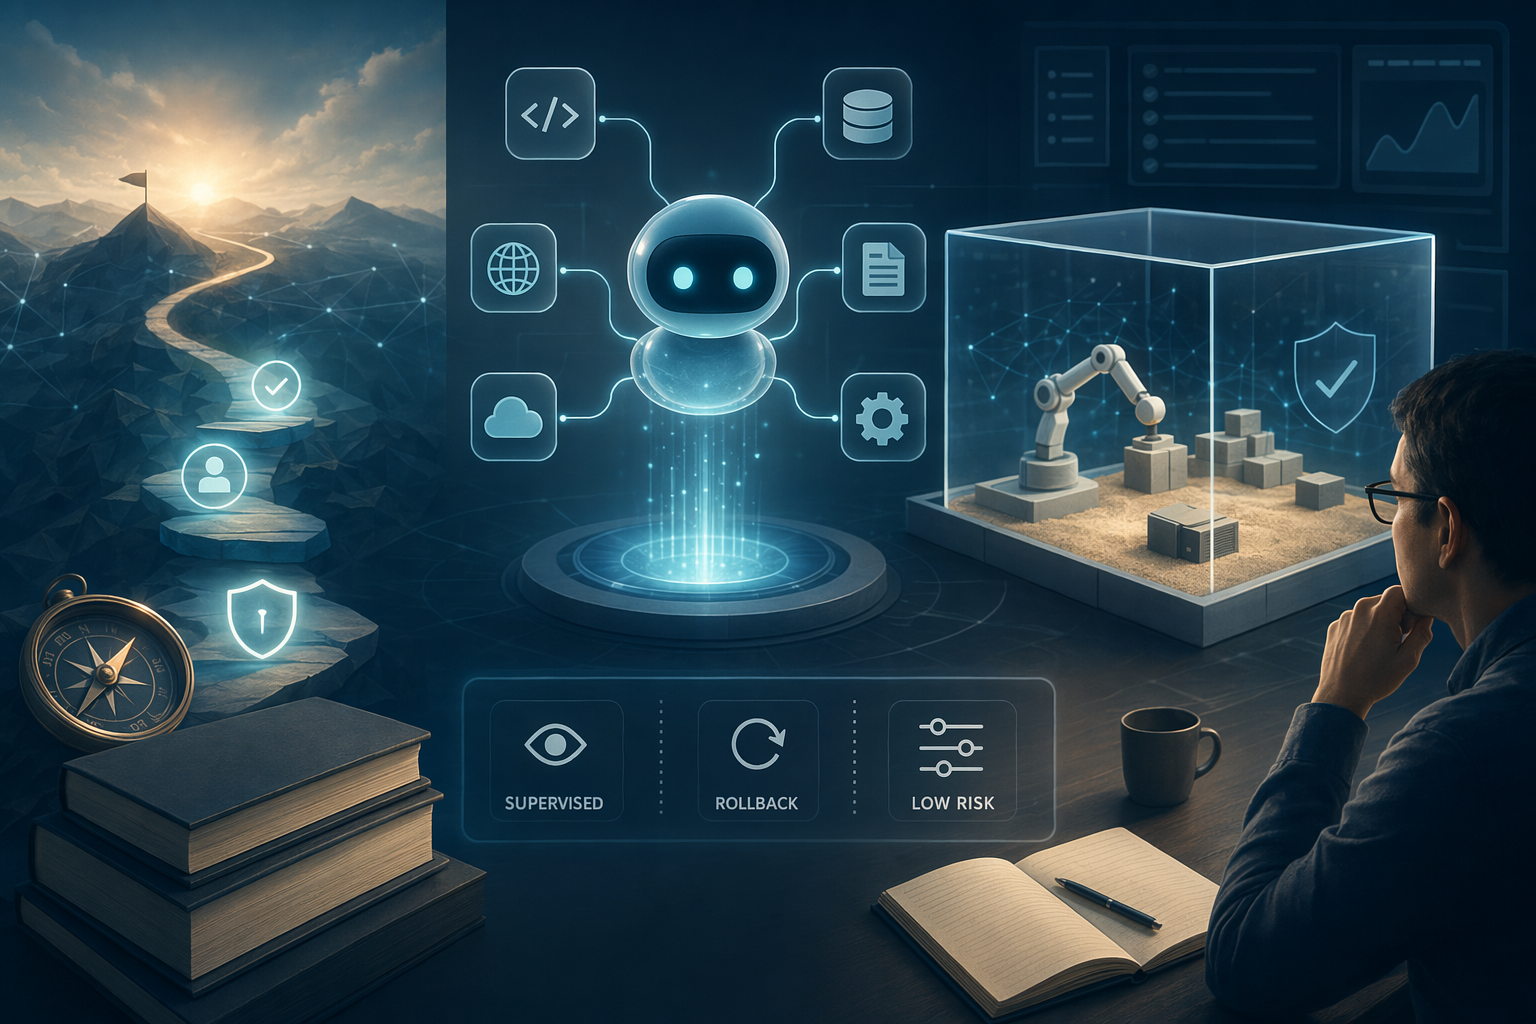
Create a landscape editorial hero image for this Studio Global article: AI Agent/Agentic AI 係乜?2025 年值唔值得用?. Article summary: 2025 年,AI agent 值得試但唔值得放手盲信:它是會用工具/API 做事的 AI 系統;MIT AI Agent Index 顯示 30 個較知名 agents 中只有 9 個有記錄到 sandboxing 或 VM isolation,所以起步應限於低風險、可監督、可回滾流程。[1][2][3]. Topic tags: ai, ai agents, agentic ai, automation, workflow automation. Reference image context from search candidates: Reference image 1: visual subject "Deloitte在《2025 AI Forum》中预测,到2025年,25%使用GenAI的公司将启动agentic AI试点,到2027年这一比例将升至50%。但Gartner的调查却显示,只有15%的IT" source context "AI Agent 2025:繁荣背后的真相——从海外主流论坛看技术演进的理性回归-腾讯云开发者社区-腾讯云" Reference image 2: visual subject "Deloitte在《2025 AI Forum》中预测,到2025年,25%使用GenAI的公司将启动agentic AI试点,到2027年这一比例将升至50%。但Gartner的调查却显示,只有15%的IT" source context "AI Agent 2025:繁荣背后的真相——从海外主流论坛看技术演进的理性回归-腾讯云开发者社区-腾讯云" Style: premium digital editorial illustration, source-backed research mood
openai.com
The real dividing line for AI agents is not whether they can chat convincingly. It is whether they can connect to tools, APIs, browsers or business systems and carry out a sequence of actions toward a goal.
NIST describes the leading AI-agent pattern as putting a general-purpose AI model inside software scaffolding so the model can manipulate tools and take action beyond simple text output. IBM makes a similar point: AI agents can call tools and APIs to meet more difficult goals, while agentic AI can obtain current data, optimize workflows and create subtasks.
That makes AI agents useful — and riskier than ordinary chatbots. A chatbot that gives a bad answer may waste time. An agent with access to real systems may update the wrong record, send the wrong message or trigger the wrong workflow. So the practical 2025 answer is: yes, AI agents are worth testing, but only in controlled pilots with clear limits.
Studio Global AI
Continue your research
This page includes a source-backed answer you can continue inside Studio Global.
What is the short answer to "What are AI agents, and are they worth using in 2025?"?
AI agents are not just chatbots. NIST describes systems that can perceive environments, use tools and take actions beyond text output, while IBM highlights tool and API use for more complex goals.[1][5]
What are the key points to validate first?
AI agents are not just chatbots. NIST describes systems that can perceive environments, use tools and take actions beyond text output, while IBM highlights tool and API use for more complex goals.[1][5] In 2025, the sensible approach is a controlled pilot: MIT’s 2025 AI Agent Index found that only 9 of 30 prominent agents had documented sandboxing or VM isolation, and only 4 of 13 high autonomy agents disclosed any a...
What should I do next in practice?
Enterprise interest is real, but ROI is not automatic. Microsoft says more than 230,000 organizations, including 90% of the Fortune 500, have used Copilot Studio to build AI agents and automations, but each workflow s...
AI agent = AI model + goal + tools or APIs + permissions + monitoring and rollback.
The model provides language understanding and reasoning. The tools and APIs let it do things: search, retrieve files, query databases, open a browser, create tickets, update records or draft actions for approval. Permissions decide what it is allowed to touch. Monitoring and rollback determine whether humans can see, stop and reverse what happened.
So when a product claims to be agentic, do not judge it by the label. Ask what it can actually do:
Does it have a defined task or goal?
Can it use tools, APIs, a browser or enterprise systems?
Does it decide the next step based on tool results?
Are there approval gates, logs, monitoring, emergency stops and rollback options? MIT’s AI Agent Index tracks control and safety fields such as approval requirements, monitoring, emergency stops, sandboxing and evaluations.
If those pieces are missing, it may be a useful AI assistant — but not necessarily an agent you should trust with operational work.
AI agent vs agentic AI
The terms overlap, and vendors do not always use them consistently. A practical distinction is:
AI agent: a specific system or product that can pursue a goal by using tools and taking actions.
Agentic AI: the broader design approach in which AI systems act more autonomously — for example by gathering current information, breaking work into subtasks and optimizing workflows.
In short: an AI agent is the system that does the work. Agentic AI is the architecture or approach that makes the system more action-oriented.
How agents differ from chatbots and automation
Type
How to tell
Best fit
Standard LLM or chatbot
Mainly generates text, answers questions, summarizes or drafts. Without tool permissions, it usually stays at the advice or content layer.
Q&A, summaries, drafts, brainstorming
Workflow automation
Steps are mostly predefined and rule-based. If the process is stable and predictable, traditional automation may be enough.
Clear rules, low variation, low error cost
AI agent
Uses tools or APIs toward a goal, adapts based on results and can take actions beyond text output.
Multi-step, cross-system processes that need some judgment but can still be supervised
If all you need is a product description, an email draft or a meeting summary, a chatbot may be enough. If you need software to check a source, open a tool, update a system, compile results and hand the final step to a person for approval, an AI agent starts to make sense.
Is it worth using in 2025?
For many teams, yes — but not as a fully autonomous digital employee. The stronger use case is a bounded pilot inside a workflow where success can be measured and mistakes can be contained.
Good first candidates usually have these traits:
The work is repetitive, but each case needs a little judgment.
The task crosses several tools, data sources or internal systems.
Inputs, outputs and success criteria are clear.
A human can review the result before anything irreversible happens.
If the agent gets it wrong, the action can be corrected, reversed or rerun.
Poor first candidates include legal decisions, medical advice, financial approvals, irreversible transactions, customer commitments or any process where one mistake creates serious harm. The reason is simple: the value of an agent comes from its ability to act through tools and systems, but that same ability increases the cost of failure.
The main risk: autonomy can outrun transparency
The MIT 2025 AI Agent Index reviewed 30 prominent AI agents using public information and correspondence with developers. It found wide differences in autonomy: chat agents generally remained at lower autonomy levels, Level 1–3; browser agents could operate at Level 4–5 with limited intervention; and enterprise agents could move from Level 1–2 in design to Level 3–5 when deployed.
The transparency gap is important. Among 13 agents showing frontier levels of autonomy, only 4 disclosed any agentic safety evaluations. The PDF version of the Index also reports that only 9 of 30 agents had documented sandboxing or VM isolation.
That does not mean every AI agent is unsafe. It means buyers and teams should not rely on polished demos alone. Before deployment, ask:
Can permissions be limited to the minimum needed?
Is there a human approval step before any irreversible action?
Are all actions logged and traceable?
Is there monitoring, an emergency stop and a rollback process?
Can the agent be tested first in a sandbox, virtual machine, test account or low-risk dataset?
If the answer is no, the tool may still be useful for drafting or analysis — but it should not be operating freely in production systems.
Adoption is real, but ROI must be measured workflow by workflow
There are credible signs that organizations are experimenting. At Microsoft Build 2025, Microsoft said more than 230,000 organizations, including 90% of the Fortune 500, had used Copilot Studio to build AI agents and automations.
That number matters, but it has limits. It is a vendor-reported adoption figure, and it includes both agents and automations. Having used or built something does not prove that every process generated a positive return.
Consulting material also frames AI agents as an operational layer for automating workflows and supporting decisions, with ROI as a driver of adoption. But external ROI claims should not replace your own baseline data.
A practical pilot should measure:
The time humans spent on the process before the agent.
The time the agent takes to complete the same work.
Error rate and rework rate.
Human review cost.
Cost of permissions, monitoring, testing and rollback.
Whether the bottleneck actually disappears, or merely shifts to the approval queue.
A five-minute checklist before you start
If most of these answers are yes, an AI-agent pilot is worth considering:
Does the workflow have clear inputs, outputs and success criteria?
Does the task truly need tools, APIs or cross-system actions — not just text generation?
Can the agent’s permissions be narrowed to only the required actions?
Can a human approve any irreversible step?
Are monitoring, logs, stop controls and rollback available?
Can testing happen first in a sandbox, virtual machine, test account or low-risk environment?
Do you have baseline data for time, error rate and cost before the pilot?
Is someone responsible for reviewing outputs, permissions and failure cases over time?
If questions 3 to 6 are hard to answer, do not put the agent into production autonomy yet. Use a chatbot, traditional workflow automation or human-in-the-loop AI assistance instead.
Bottom line
AI agents matter because they move AI from answering questions to using tools to complete work. That is a real step forward. It is also why they need stricter controls than ordinary chatbots.
In 2025, the best strategy is not to hand an agent the keys to the business. Start with one low-risk, reviewable, reversible workflow. Measure your own data. Expand only when the agent saves time without increasing hidden review work, error risk or operational exposure. That is more reliable than trusting a generic ROI claim — and more consistent with the safety and transparency evidence available so far.
Microsoft Build 2025: The age of AI agents and building the open ...